# Installation Guides
Connecting Sophos, Fortigate, Palo Alto, MikroTik and Ruijie devices to Useroam
# Sophos Integration Guide
This guide covers the full integration between a **Sophos Firewall** and Useroam Cloud: RADIUS authentication, web authentication, the captive portal template, the firewall rules, and 5651 syslog forwarding.
> **Before you start:** you need administrator access to the Sophos web interface and the WAN IP address of the firewall. If Useroam will also manage users over the API, complete the **Sophos API Connection** page afterwards.
---
### **1 - Adding the device to the Useroam panel**
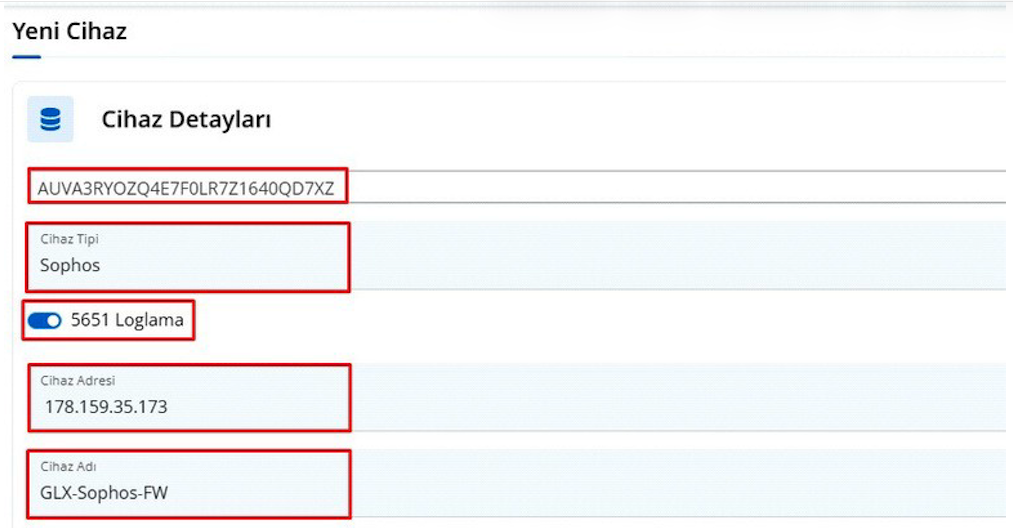
Sign in to your panel at **[panel.useroam.com](https://panel.useroam.com)** and add a **New Device**. The system selects your license automatically.
- **Device type:** select **Sophos**.
- **Device address:** enter the WAN IP address of the firewall. If you have more than one WAN IP, the Sophos device sends this request from the first WAN interface by default.
`Note: if you want the traffic to leave over a different WAN interface, create an SNAT rule to route it through the interface you want.`
---
### **2 - Device Access settings**
Go to **Administration > Device Access**. For the zone where you will use Useroam, enable **only** the **Captive Portal** and **DNS** options.
**Caution:** if you enable other authentication mechanisms such as RADIUS SSO at the same time, you may run into redirection problems or a slow-loading captive portal page.
---
### **3 - Adding the RADIUS server**
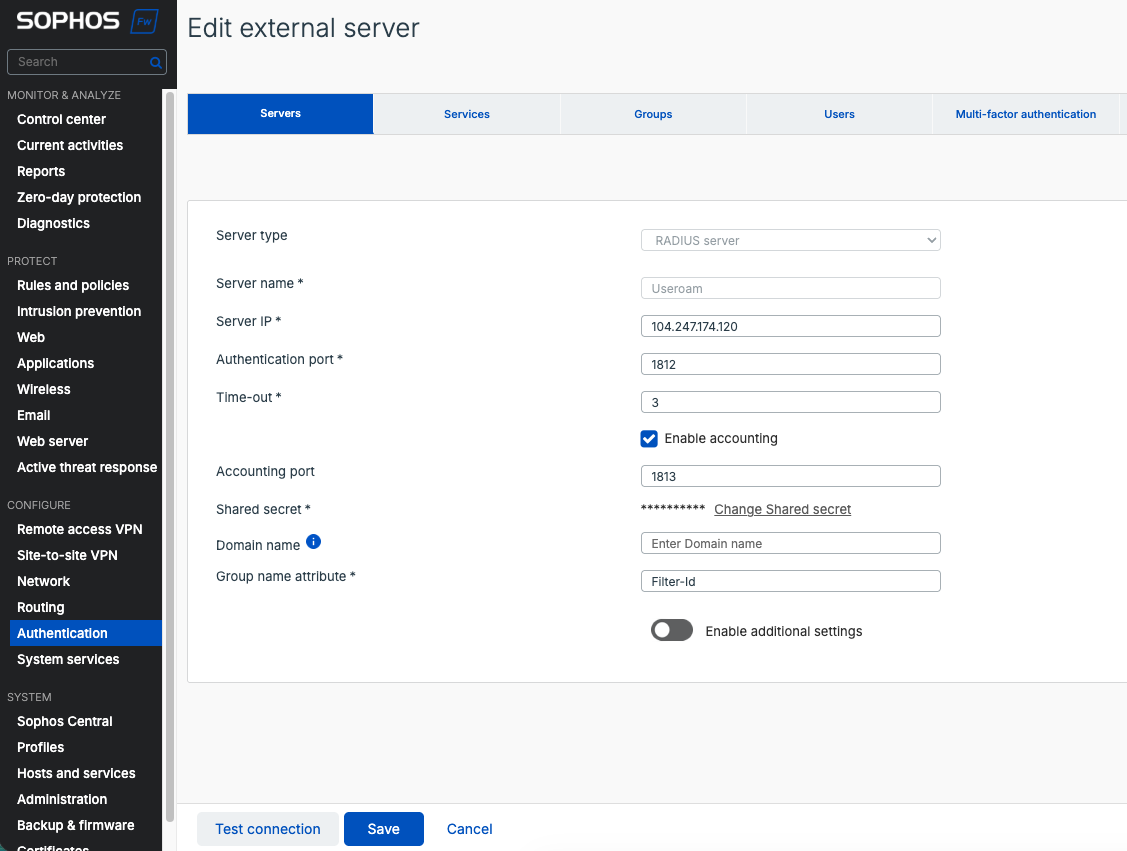
Add a new RADIUS server from **Authentication > Servers**. In the Server IP field, enter the IP address you get when you ping **panel.useroam.com**.
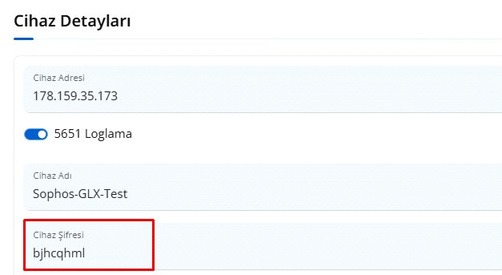
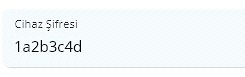
Then copy the code shown next to **Device Password** under **Useroam > Settings > Device Settings** and paste it into the **Shared Secret** field.
[](https://help.useroam.com/uploads/images/gallery/2026-07/screenshot-2026-07-06-at-11-34-24.png)
---
### **4 - Connection test (optional)**
If you want to test at this point: create a new user in the Useroam Cloud panel via **Guests > New User**, then check the connection with **Test Connection** inside the RADIUS server settings on the firewall.
---
### **5 - Authentication priority (Authentication Methods)**
Go to **Authentication > Services**, move Useroam to the top of the *Firewall Authentication Methods* list, and click **Apply** to save.
---
### **6 - Web authentication settings**
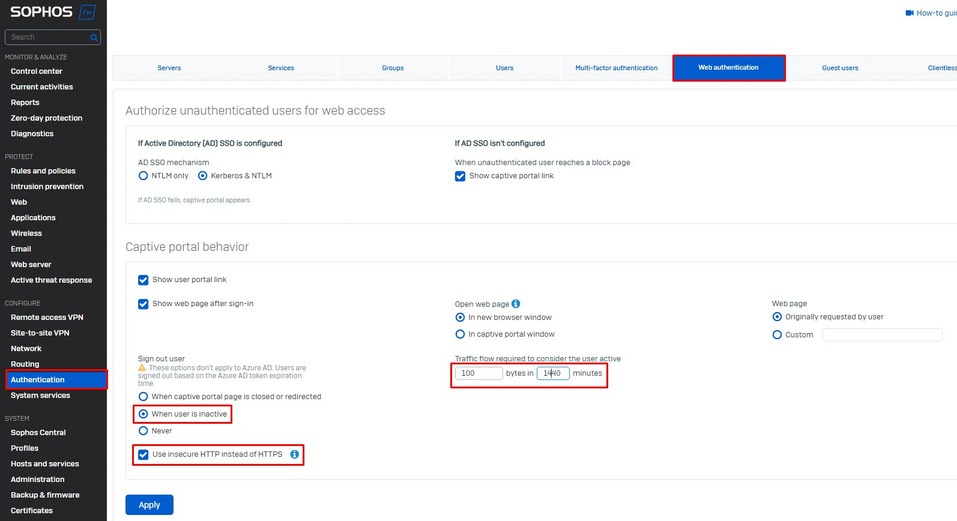
Move on to **Authentication > Web Authentication**. Under *Sign Out User*, tick **When User is Inactive**.
In the *Traffic flow* section next to it, set **1440 minutes** (24 hours) for 100 bytes. With this setting, every connected device stays signed in on the firewall as long as it transfers at least 100 bytes within 24 hours. You can shorten this period if you prefer.
Finally, tick **"Use insecure HTTP instead of HTTPS"** and save.
---
### **7 - Integrating the captive portal design (Custom HTML)**
In Useroam, go to **Settings > Device Settings** and copy the whole block that starts with the `` line. Paste it into **Authentication > Web Authentication > Captive portal appearance > Custom HTML** on the Sophos firewall and save.
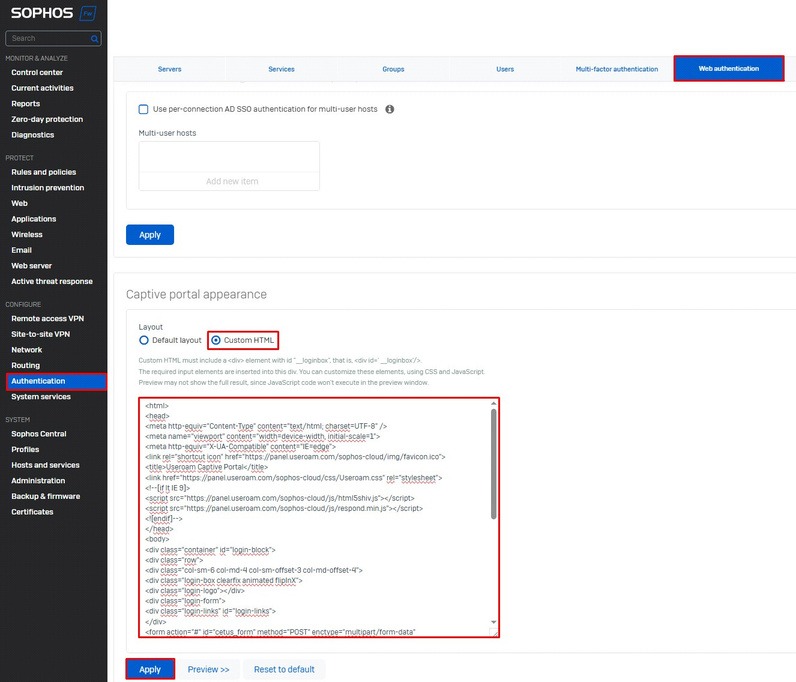
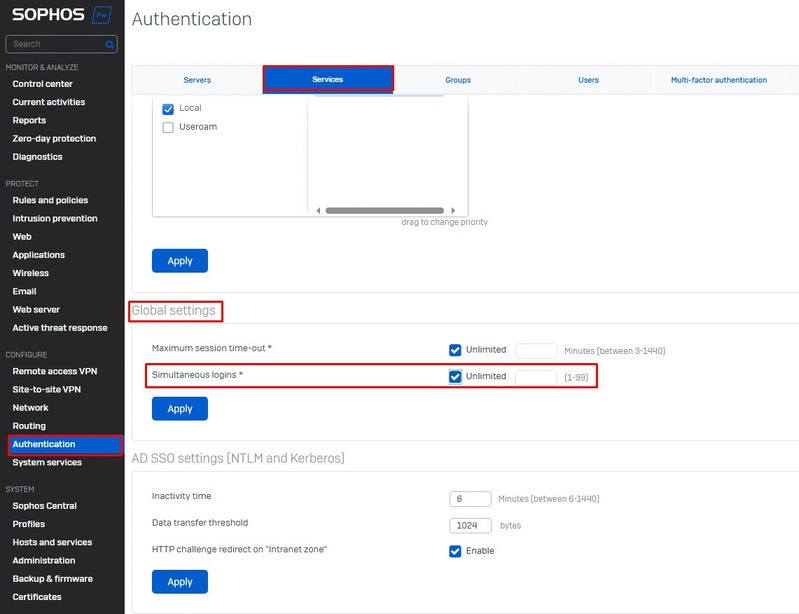
**Limiting concurrent sessions:** if you want to limit how many devices can use a single account, configure this under **Configure > Authentication > Services > Global Settings** on the Sophos firewall. By default the system allows an unlimited number of devices.
---
## Creating the firewall rules
To create the rules, go to **Protect > Rules and Policies** on the Sophos firewall and open the **Add Firewall Rule** page.
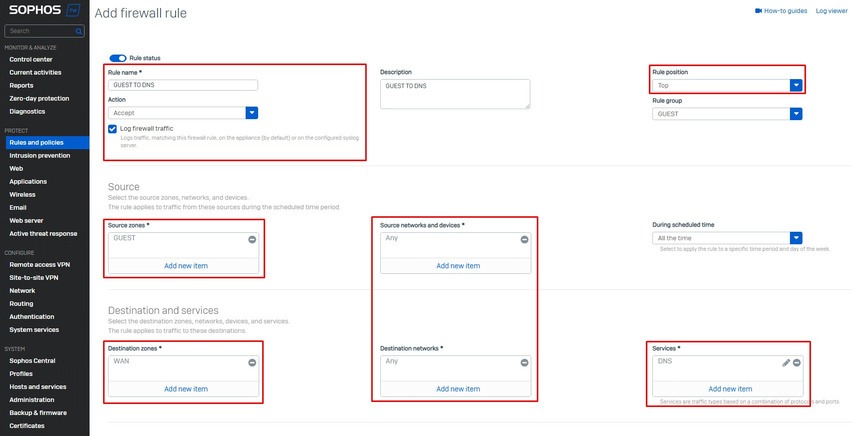
#### **RULE 1: Guest to DNS**
Every device sends a DNS query to a vendor-specific domain to work out whether the network it joined has internet access (for example `captive.apple.com`).
When the answer comes back, the device concludes it has internet and starts passing traffic. Without it, the hotspot redirect will not happen.
**This rule must sit above the guest internet access rule.**
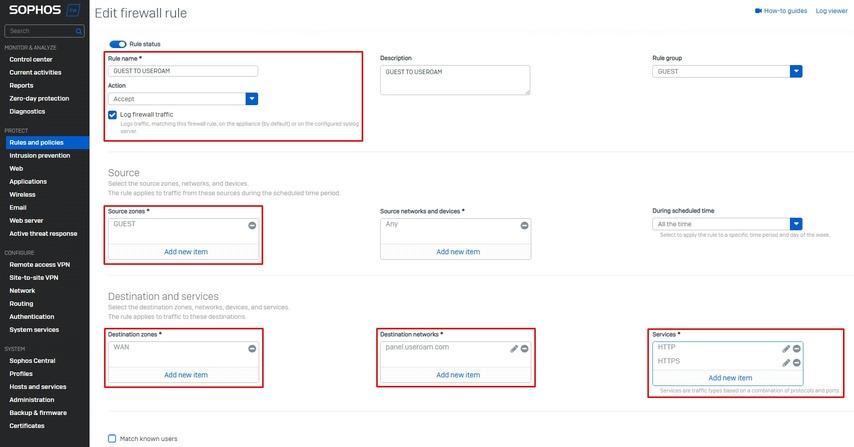
#### **RULE 2: Guest to Useroam**
This rule lets devices on your guest network reach `*.useroam.com`. Selecting **HTTP/HTTPS** under Services is enough.
[](https://help.useroam.com/uploads/images/gallery/2026-07/useroam-cloud-sophos-entegrasyon-kilavuzu-pdf-1-pdf-55.jpg)
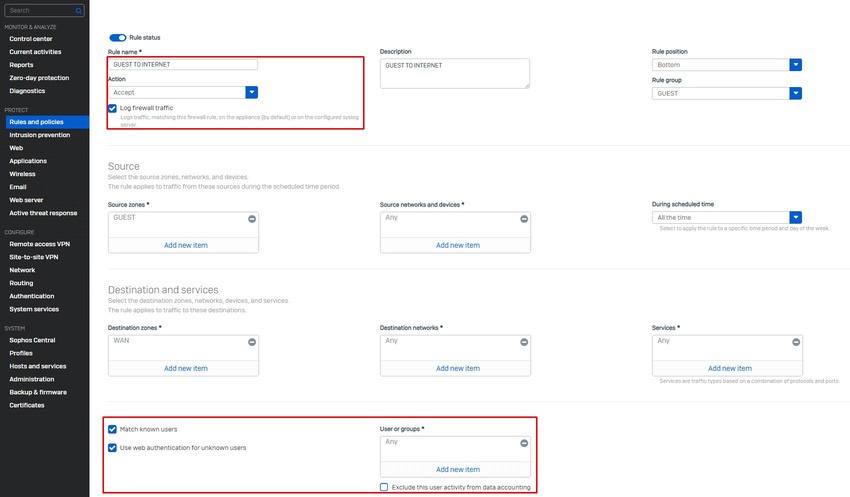
#### **RULE 3: Guest to Internet**
This rule provides internet access for your devices.
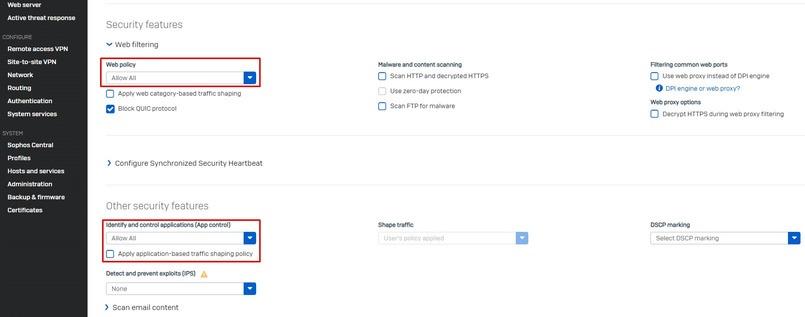
Tick the **Log Firewall** checkbox. So that unknown users are shown the hotspot screen, also tick **Match Known Users** and **Use Web Authentication For Unknown Users**. For Web Policy and Identify And Control Applications (App Control), select *Allow All* or any policy you prefer.
[](https://help.useroam.com/uploads/images/gallery/2026-07/useroam-cloud-sophos-entegrasyon-kilavuzu-pdf-1-pdf-63-1.jpg)
*When you are done, the **Protect > Rules and Policies** list should be ordered as shown below.*
---
## Forwarding logs to the Useroam device
#### **1 - Defining the syslog server**
First go to **System Services > Log Settings** and define a new syslog server.
#### **2 - Entering the syslog details and starting**
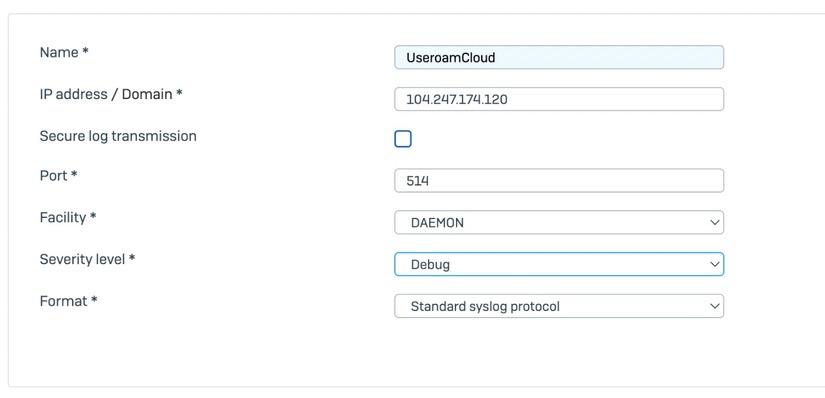
Fill in the following details for the newly added syslog server:
- **Name:** Useroam Cloud
- **IP address / Domain:** `104.247.174.120`
- **Port:** `514`
- **Facility:** DAEMON
- **Severity level:** Debug
- **Format:** Standard syslog protocol
[](https://help.useroam.com/uploads/images/gallery/2026-07/useroam-cloud-sophos-entegrasyon-kilavuzu-pdf-1-pdf-75.jpg)
Then, on the row for the newly added syslog server, select **only** the **Content Filtering** fields to start sending logs to Useroam.
#### **3 - Checking the log packets**
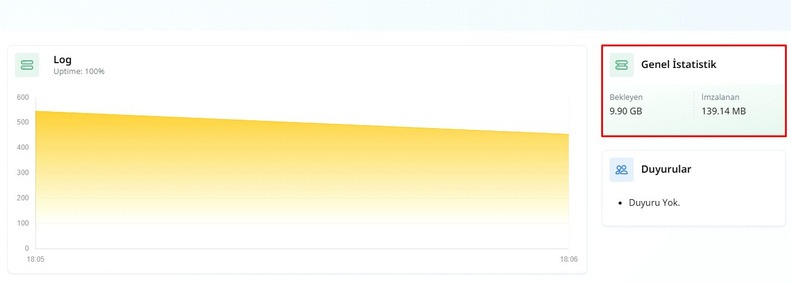
Afterwards, go back to the Useroam panel to confirm that packets are arriving from the firewall. Check the **General Statistics** area in the top-right corner and look at the section under **Pending Signature**.
---
#### **Important — integration complete**
Your Sophos integration is complete. If you run into any problems during the process, contact our support team at **destek@useroamteknoloji.com**.
---
## Login with WhatsApp — firewall allowlist (walled garden)
For the **Login with WhatsApp** flow to work while the guest is still behind the captive portal (before internet access is granted), the following addresses **must be allowed** in your firewall or walled-garden configuration. Without these rules the WhatsApp login screen will not open and the automatic login based on delivery confirmation will not work.
### Domains to allow (FQDN)
- `*.wa.me`
- `*.whatsapp.com`
- `*.whatsapp.net`
- `g.whatsapp.net`
- `mmg.whatsapp.net`
- `fbsbx.com`
- `*.useroam.com`
### IP addresses to allow
- `157.240.0.0` — Meta / Facebook network block
- `31.13.0.0` — Meta / Facebook network block
- `104.247.174.120` — Useroam panel
**Note:** `157.240.0.0` and `31.13.0.0` are typically `/16` network blocks (Meta infrastructure); we recommend defining them as blocks in the firewall (`157.240.0.0/16`, `31.13.0.0/16`). `104.247.174.120` is the Useroam panel IP (`/32`). Use the domain list if your firewall supports FQDN-based filtering; otherwise use the IP blocks.
# Fortigate Integration Guide
This guide covers the full integration between a **FortiGate firewall** and Useroam Cloud: RADIUS authentication, the captive portal replacement messages, the firewall policies, and 5651 syslog forwarding.
> **Before you start:** you need administrator access to the FortiGate web interface (and CLI access if a second syslog server is required), plus the WAN IP address of the firewall.
---
### **1 - Adding the device to the Useroam panel**
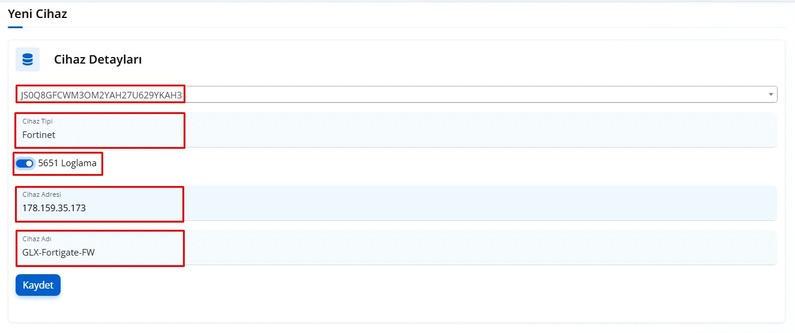
Sign in to your panel at **[panel.useroam.com](https://panel.useroam.com)** and add a **New Device**. The system selects your license automatically.
- **Device type:** select **Fortinet**.
- **Device address:** enter the WAN IP address of the firewall. If you have more than one WAN IP, the firewall usually sends this request from the first WAN interface by default.
`Note: if you want the traffic to leave over a different WAN interface, create an SNAT rule to route it through the interface you want.`
---
### **2 - Adding the RADIUS server**
On your firewall, go to **User & Authentication > RADIUS Servers** and click **Create New** to define the Useroam Cloud server.
- **Authentication method:** Specify / PAP
- **Primary Server IP/Name:** `panel.useroam.com`, or by IP address: `104.247.174.120`
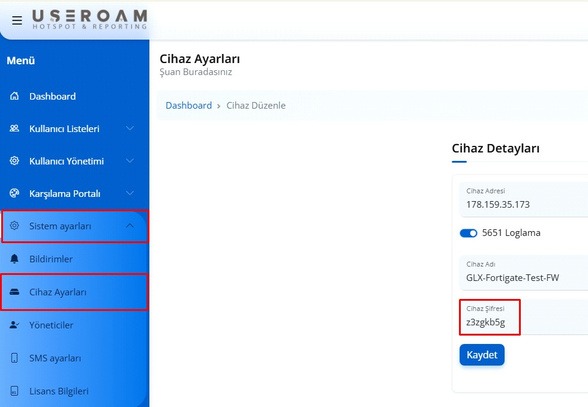
- **Secret:** after adding the device in Useroam Cloud, copy the automatically generated **device password** from **Settings > Device Settings** and paste it here.
`Test Connectivity: you can run a RADIUS test from your firewall against Useroam Cloud.`
---
### **3 - Captive portal messages (Replacement Messages)**
Three fields under **System > Replacement Messages** need their code replaced. Switch to **Extended View** from the top-right corner first.
#### **3A - Login Failed Page**
Search for **Login Failed Page**. On the screen that opens, clear the code area on the right, paste in `{"Error":"passwordwrong", "ErrorType":"passwordwrong"}` and save.
#### **3B - Authentication Success Page & Login Page**
Search for **Authentication Success Page**. Clear the code area on the right, paste in `{"Error":"success", "ErrorType":"success"}` and save.
Finally, for **Login Page**, paste the entire code you copied from the Useroam Cloud panel (**Settings > Device Settings**).
---
### **4 - Creating the user group (User Groups)**
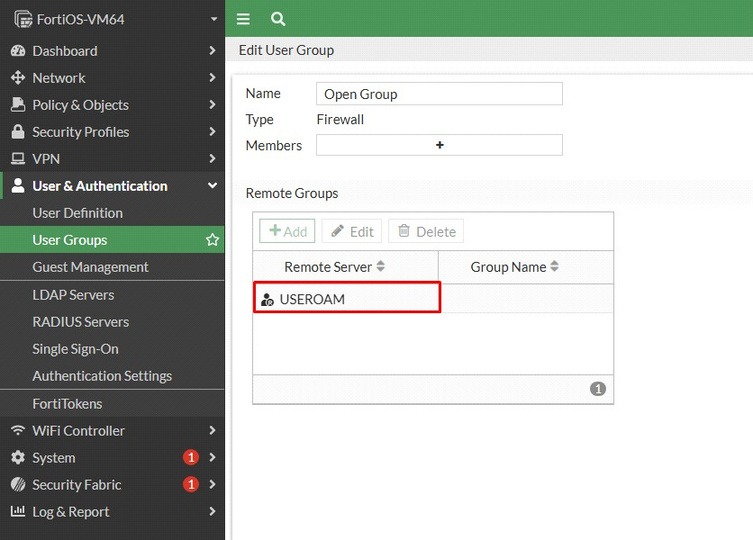
Go to **User & Authentication > User Groups** and create a group for Useroam Cloud.
---
### **5 - Interface configuration**
On the firewall, edit the relevant port from the **Interface** menu.
- **DNS Server:** first enter the firewall's gateway IP for this interface, then define the DNS servers.
- **Security Mode:** enable **Captive Portal**.
- **User Access:** Restricted to Groups
- **User Groups:** select the group you created in the previous step (for example *Open Group*).
- **Exempt destinations/services:** create an FQDN object for `panel.useroam.com` and select it.
---
## Creating the firewall policies
To create the rules, go to **Policy & Objects > Firewall Policy** on the FortiGate firewall.
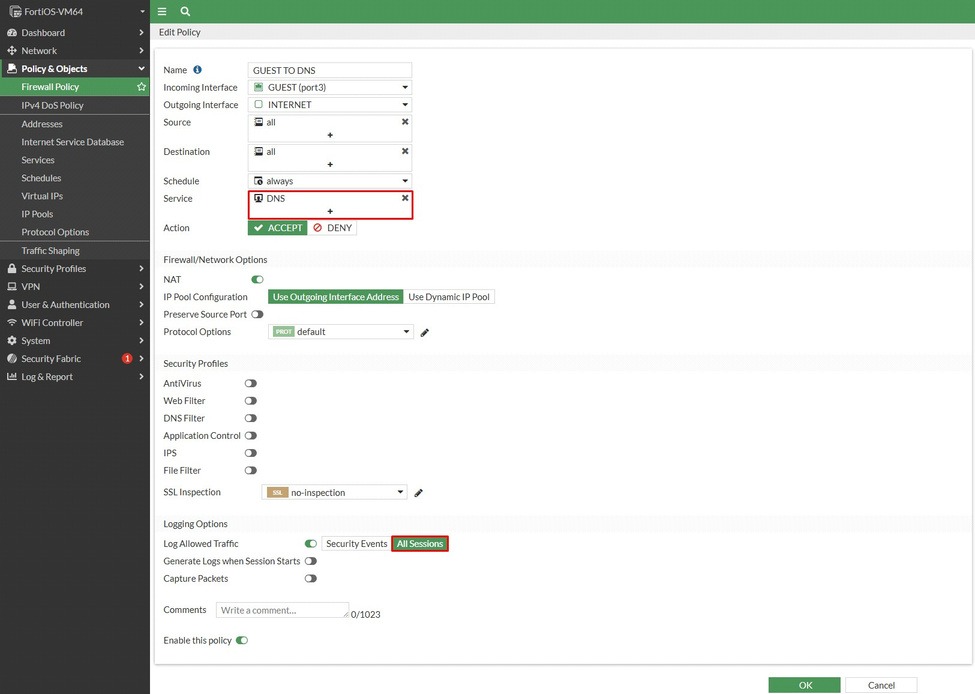
#### **RULE 1: Guest to DNS**
Create your DNS rule first. Selecting only the **DNS** service is enough.
#### **RULE 2: Guest to Useroam**
This rule lets users in the zone where you enable Useroam reach the **panel.useroam.com** panel. Under Service, select the **HTTP/HTTPS** services.
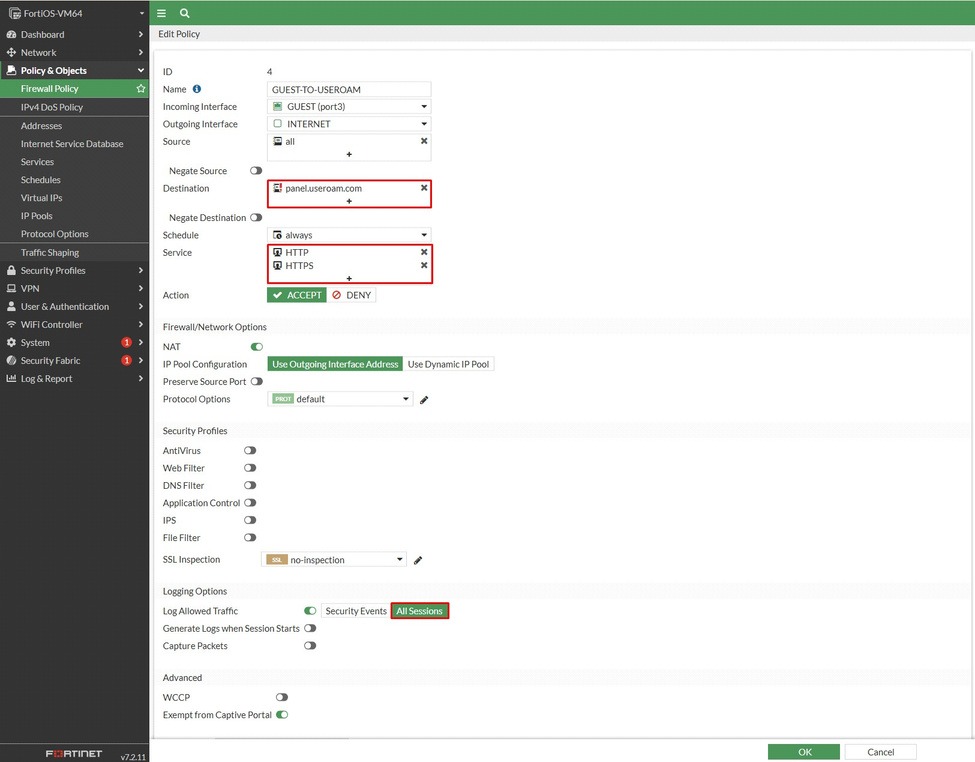
#### **RULE 3: Guest to Internet**
This rule is your general internet access rule. Add the **User Group (Open Group)** object you created as the Source, and the **ALL** service under Service.
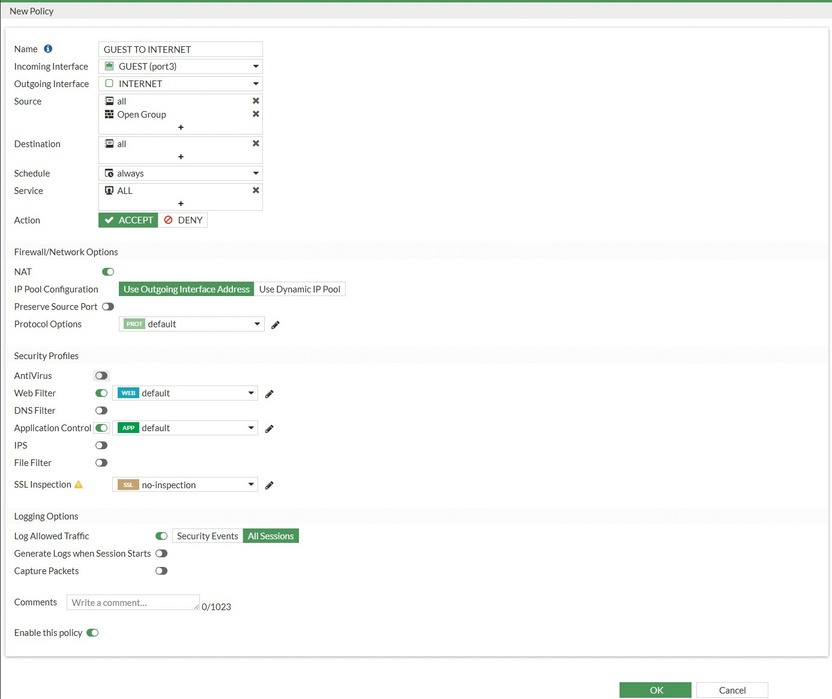
*Once all three rules are in place, the **Policy & Objects > Firewall Policy** list should be ordered as shown below.*
---
## Forwarding logs to the Useroam device
Under **Log & Report > Log Settings**, set **Syslog logging** to **Enable**. Then enter the server details in the IP Address/FQDN field as **panel.useroam.com**.
**Caution:** if a different IP is already defined here, you must configure your second syslog server from the command line (CLI).
After checking whether `syslogd2` already contains another configuration, you can use the example command block below:
`config log syslogd2 setting`
`set status enable`
`set server "panel.useroam.com"`
`set port 514`
`set format default`
`end`
---
#### **Important — integration complete**
That's it — your FortiGate integration is complete. If you run into any problems during the process, contact our support team at **destek@useroamteknoloji.com**.
---
## Login with WhatsApp — firewall allowlist (walled garden)
For the **Login with WhatsApp** flow to work while the guest is still behind the captive portal (before internet access is granted), the following addresses **must be allowed** in your firewall or walled-garden configuration. Without these rules the WhatsApp login screen will not open and the automatic login based on delivery confirmation will not work.
### Domains to allow (FQDN)
- `*.wa.me`
- `*.whatsapp.com`
- `*.whatsapp.net`
- `g.whatsapp.net`
- `mmg.whatsapp.net`
- `fbsbx.com`
- `*.useroam.com`
### IP addresses to allow
- `157.240.0.0` — Meta / Facebook network block
- `31.13.0.0` — Meta / Facebook network block
- `104.247.174.120` — Useroam panel
**Note:** `157.240.0.0` and `31.13.0.0` are typically `/16` network blocks (Meta infrastructure); we recommend defining them as blocks in the firewall (`157.240.0.0/16`, `31.13.0.0/16`). `104.247.174.120` is the Useroam panel IP (`/32`). Use the domain list if your firewall supports FQDN-based filtering; otherwise use the IP blocks.
# Palo Alto Integration Guide
This guide covers the full integration between a **Palo Alto firewall** and Useroam Cloud: zone and interface configuration, RADIUS authentication, certificates, the Authentication Portal, DNS, log forwarding, and the firewall rules.
> **Before you start:** you need administrator access to the Palo Alto web interface, the external interface IP address the firewall will use to talk to Useroam, and your SSL certificate together with its key file and password.
---
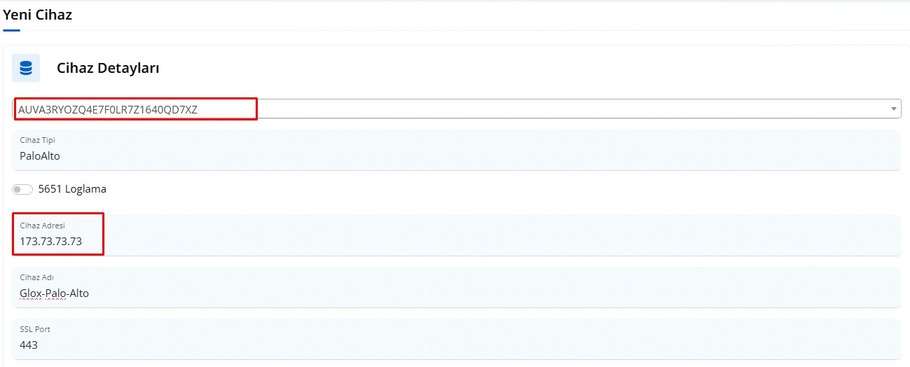
### **1 - Adding the firewall to the panel**
First sign in to your panel at **[panel.useroam.com](https://panel.useroam.com)** and add a **New Device**. In the **Device Address** field, enter the external interface IP address the firewall will use to communicate.
- **Device type:** select **PaloAlto**.
- **5651 Logging:** tick the 5651 Logging checkbox.
---
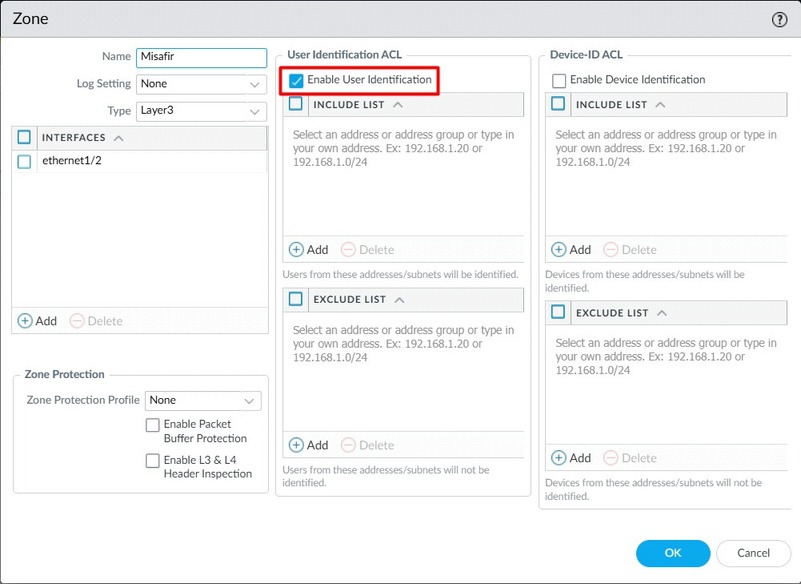
### **2 - Zone settings**
For the interface where Useroam will be enabled, create a new zone under **Network > Zone** and tick **Enable User Identification**.
---
### **3 - Interface and profile settings**
On the interface where Useroam will be enabled, create a new profile from the **Advanced** section. While doing so, tick the **Response Pages** checkbox.
---
### **4 - RADIUS settings**
Apply the settings below under **Device > Server Profiles > RADIUS**:
- **Authentication Protocol:** PAP
- **RADIUS Server / FQDN:** `panel.useroam.com`
- **Secret:** the device password you obtained from **Settings > Device Settings** in panel.useroam.com
---
### **5 - Authentication Profile**
Define the new profile under **Device > Authentication Profile**.
- **Type:** RADIUS
- **Server Profile:** select the RADIUS server profile you created.
- **Retrieve user group from RADIUS:** make sure this checkbox is ticked.
- **Advanced:** add the `all` object to the Allow List.
---
### **6 - Certificate configuration**
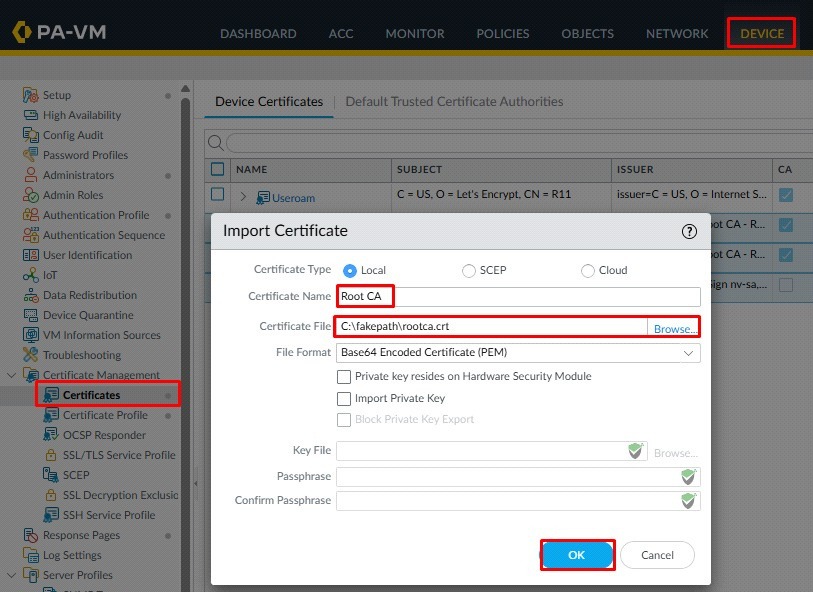
Before the certificates are installed on the device, the relevant root certificates (Root CA or Intermediate) must already be added to the system. This completes the certificate trust chain and prevents SSL/TLS errors on the client devices that connect.
#### **6A - Importing the Root CA**
As the first step, import the Root CA or CA certificate.
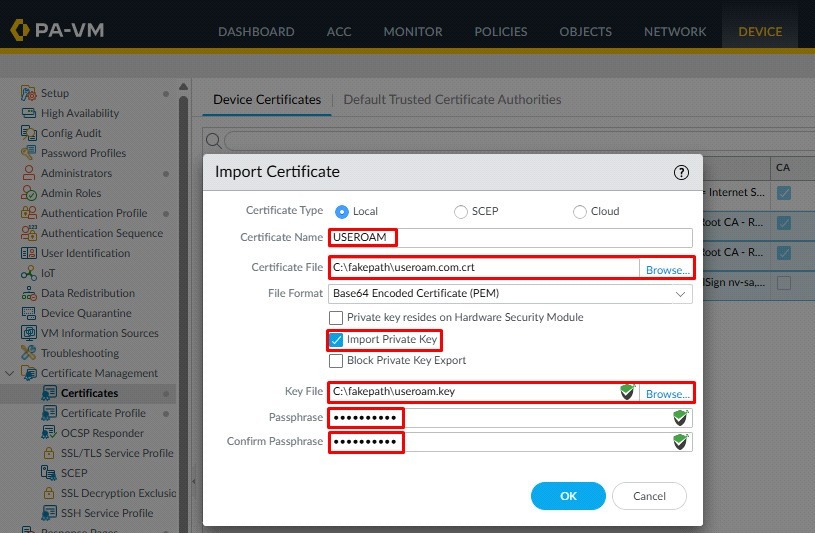
#### **6B - Uploading the certificate and key file**
Next, upload the certificate file to the firewall together with the key file and its password.
#### **6C - Verifying the layered certificate chain**
Once the upload is complete, the view should show a layered structure — a certificate chain in which the entries are linked to one another.
---
### **7 - Authentication Portal settings**
Next, open the **Settings** section under **Device > User Identification > Authentication Portal**.
- **Enable Authentication Portal:** tick this option to activate the hotspot.
- **Idle Timer and Timer:** enter the maximum value, **1440 minutes** (24 hours), in both fields. This means a user sees the hotspot screen only once a day. We use this value because we want the hotspot screen to appear once every 24 hours; if you prefer shorter sessions, adjust it to suit your needs.
- **SSL/TLS Service Profile:** select the SSL profile you created earlier. Note that on some Palo Alto versions, previously created profiles may not appear in this field. In that case, use the **New** option to create a new SSL/TLS profile from this screen. If your system does let you select one, you can use the existing profile.
If you need to create a new profile, follow these steps:
- Give the profile a name and select the SSL certificate to be used.
- Under **Protocol Settings**, choose the minimum and maximum SSL/TLS versions you want to support.
- When the settings are complete, click **OK** to save the profile.
- **Authentication Profile:** continue by selecting the Useroam profile you created.
- **Session Cookie / Timeout:** enter **1440 minutes** (24 hours) here as well, matching the value set above.
- **Redirect Host:** enter the subdomain here, since the redirect is performed over the certificate.
---
### **8 - Uploading the captive portal design (Comfort Page)**
In panel.useroam.com, go to **Settings > Device Settings** and copy the entire code block that starts with ``. Paste it into a text editor and save it in HTML format under a name such as `captive.html`. Then upload that document on the firewall via **Device > Response Pages > Captive Portal Comfort Page**.
---
### **9 - DHCP settings**
So that DNS queries from the internal network are handled without problems, the DHCP and DNS Proxy configuration must be updated if you do not have a separate DNS server. Go to **Network > DHCP > Options**.
- **Primary DNS:** enter the firewall's own interface IP address.
- **Secondary DNS:** you can define a global DNS server (for example `8.8.8.8` — Google DNS).
**Note:** if you already have an internal DNS server, add the record required for the domain redirect to your internal DNS as well (in the Static Entries section) and continue from step 11.
---
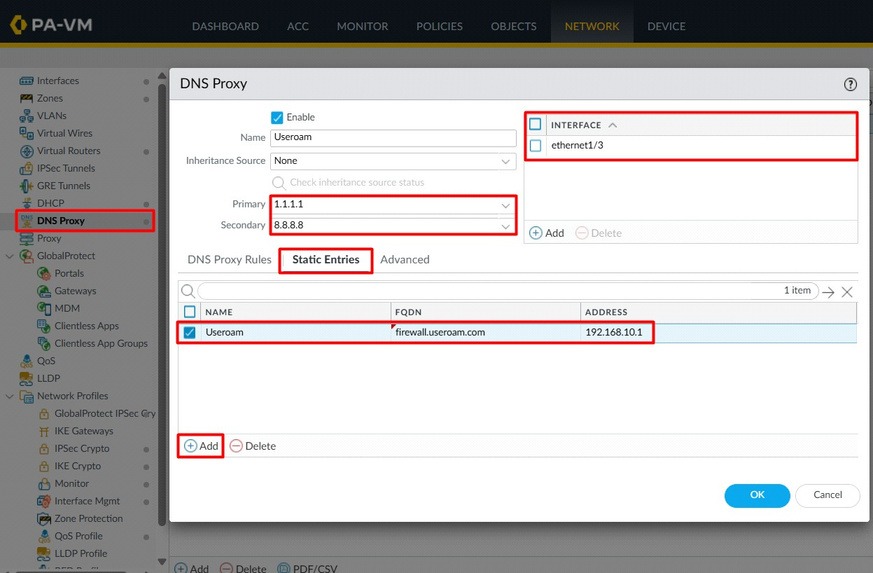
### **10 - DNS Proxy settings**
Next, define a new proxy under **Network > DNS Proxy** so DNS queries resolve correctly.
- **Interface:** select the interface(s) where Useroam will be active.
- **Primary / Secondary DNS:** enter the global DNS servers.
- **Static Entries:** click **Add** to create a new record. At this stage it is important that the IP used for the redirect is the gateway IP address of the firewall's Management Interface.
---
### **11 - Forwarding logs to Useroam (Log Forwarding)**
Go to **Objects > Log Forwarding** and add a new profile with **Add**. A separate profile must be created for each of the five log types (auth, data, decryption, traffic, url). For every entry, remember to select the Useroam profile in the Syslog section.
---
## Creating the firewall rules
Two sets of rules are needed for the Palo Alto integration. When you first create the rules, Palo Alto needs to learn the traffic — so set **Service** to `Any` at first and change it to `application-default` afterwards.
#### **12A - RULE SET 1: Authentication rules**
Go to **Policies > Authentication** and define the three rules below. **Useroam** must be selected in the Log Forwarding field on every rule.
- **RULE 1 (Allow DNS):** created so DNS queries pass through the authentication stage without problems. All DNS queries towards the WAN are allowed by selecting `default-no-captive-portal` under Authentication Enforcement.
- **RULE 2 (Allow Useroam Cloud):** this rule provides trouble-free access to Useroam Cloud. In the Destination Address field, select the `UseroamCloud` (panel.useroam.com) FQDN address object you created.
- **RULE 3 (Captive redirect):** the main rule that redirects HTTP and HTTPS traffic of users who have not yet signed in — or who are joining the network for the first time — to `default-web-form`, i.e. the captive portal screen.
#### **12B - RULE SET 2: Security rules**
Go to **Policies > Security**. On every rule, **Log at Session End** must be selected under Log Settings and **Useroam** must be assigned in Log Forwarding.
- **RULE 1 (Allow WAN DNS):** lets every device run DNS queries over the WAN without being caught by the captive portal. It is required so the device can reach its own global captive-detection domain (for example `captive.apple.com`), conclude that internet access exists, and then trigger the hotspot screen.
- **RULE 2 (Allow Useroam access):** defined so devices in the captive portal zone can reach panel.useroam.com through the firewall without problems.
- **RULE 3 (Allow internet access):** the final rule that gives your guest network internet access. On this rule, the **Source User** value in the Source section must be set to `known-user`.
> **Additional technical note (disconnecting a signed-in user):** to end an active guest session or clear its cache, sign in to the Palo Alto CLI and run the following commands in order.
>
> To list all signed-in active users and their IP addresses:
> `show user ip-user-mapping all`
>
> To drop the relevant IP address from the network, run:
> `clear user-cache ip `
> `debug user-id reset captive-portal ip-address `
---
#### **Important — integration complete**
That's it — your Palo Alto integration and server change are complete. If you run into any technical problems during the process, contact our support team at **destek@useroamteknoloji.com**.
---
## Login with WhatsApp — firewall allowlist (walled garden)
For the **Login with WhatsApp** flow to work while the guest is still behind the captive portal (before internet access is granted), the following addresses **must be allowed** in your firewall or walled-garden configuration. Without these rules the WhatsApp login screen will not open and the automatic login based on delivery confirmation will not work.
### Domains to allow (FQDN)
- `*.wa.me`
- `*.whatsapp.com`
- `*.whatsapp.net`
- `g.whatsapp.net`
- `mmg.whatsapp.net`
- `fbsbx.com`
- `*.useroam.com`
### IP addresses to allow
- `157.240.0.0` — Meta / Facebook network block
- `31.13.0.0` — Meta / Facebook network block
- `104.247.174.120` — Useroam panel
**Note:** `157.240.0.0` and `31.13.0.0` are typically `/16` network blocks (Meta infrastructure); we recommend defining them as blocks in the firewall (`157.240.0.0/16`, `31.13.0.0/16`). `104.247.174.120` is the Useroam panel IP (`/32`). Use the domain list if your firewall supports FQDN-based filtering; otherwise use the IP blocks.
# MikroTik Integration Guide
## Video walkthrough
You can watch the setup in the video first. Below the video you will find the same setup written out step by step, with screenshots.
## What is it for?
This guide shows how to connect a MikroTik router to Useroam and set up guest Wi-Fi login (hotspot), the Useroam login connection (RADIUS) and 5651 legal logging. The setup has two parts:
1. **Connecting the device to the panel:** you paste a single line into the device terminal. It only makes the minimum change needed for the panel to connect securely; your existing configuration is not touched.
2. **Setting up the guest network:** the panel reads your device, asks which port should carry the guest network and generates a setup code made for your device. After you read and approve it, you apply it with one more line.
> **Do not want to expose your router to the internet?** In the automatic setup described here, the panel connects to your router over the internet. If you want the router to stay closed from outside, or the panel cannot reach it, follow [Setting up MikroTik without exposing it to the internet (offline)](/books/installation-guides/page/setting-up-mikrotik-without-exposing-it-to-the-internet-offline) instead. On the offline path the panel asks you two questions (the names of the guest interface and the internet uplink), prepares the setup script and gives you a single line to paste into the terminal. When adding a new device, just choose **Offline** as the **Setup method**, or press **Device closed to the internet? Offline setup** under **Device Settings** > **Setup**.
## When do you use it?
- You are connecting a new MikroTik device to Useroam for the first time.
- You set a device up the old way (uploading hotspot files by hand) and want to move it to the new setup.
- You reset or replaced the device and need to connect it again.
## Before you start
- **The address the device uses to reach the internet must match the Device Address saved in the panel.** The setup code only accepts requests from that address. This is the most common problem. If your device sits behind another modem, the panel must hold the modem's public address.
- **The panel must be able to reach your device from outside.** If the device faces the internet directly nothing else is needed (port 443). If it sits behind another modem or firewall, add a port forward there: an external port (e.g. *8443*) must go to port *443* of the MikroTik. You will enter the external port in the **Access port** field. If that is not possible (for example a carrier shared IP, CGNAT), use the [offline setup](/books/installation-guides/page/setting-up-mikrotik-without-exposing-it-to-the-internet-offline).
- **RouterOS 7.1 or newer** is required. RouterOS 6 has no REST API, so the panel cannot manage it.
- **On RouterOS 7.23.3 and above** you must first enable advanced device mode and unplug and replug the device (step 3). You can check your version in the terminal with `/system resource print`.
- You need administrator access to the device with **Winbox** or **SSH** (to open a terminal).
- The device must be added in the panel. If it is not, start at step 1.
## Step by step
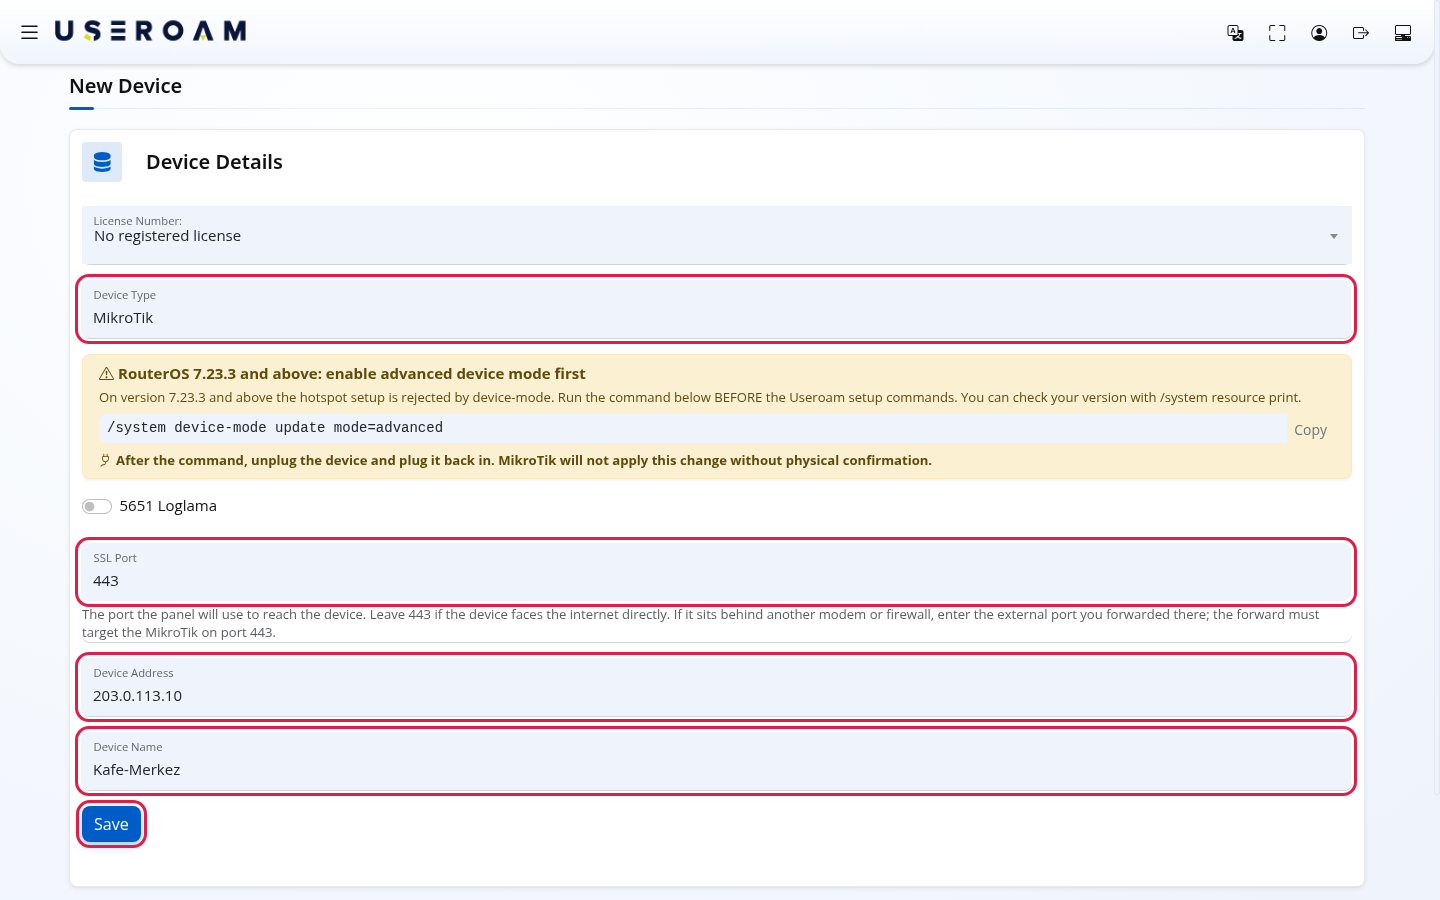
1. **Add the device to the panel.** On the **Device Selection** screen press **New Device**. Choose **MikroTik** as **Device Type**. In the **Setup method** that appears below it, keep **Automatic** selected (the path of this guide). Leave **SSL Port** at *443* if the device faces the internet directly, or enter the forwarded external port if it sits behind a modem. Enter the device's public IPv4 address in **Device Address** (e.g. *203.0.113.10*) and the name you want to see in the panel in **Device Name** (e.g. *Kafe-Merkez*), switch on **5651 Loglama** and press **Save**. All fields of this form are on the [Adding a New Device](/books/settings/page/adding-a-new-device) page.
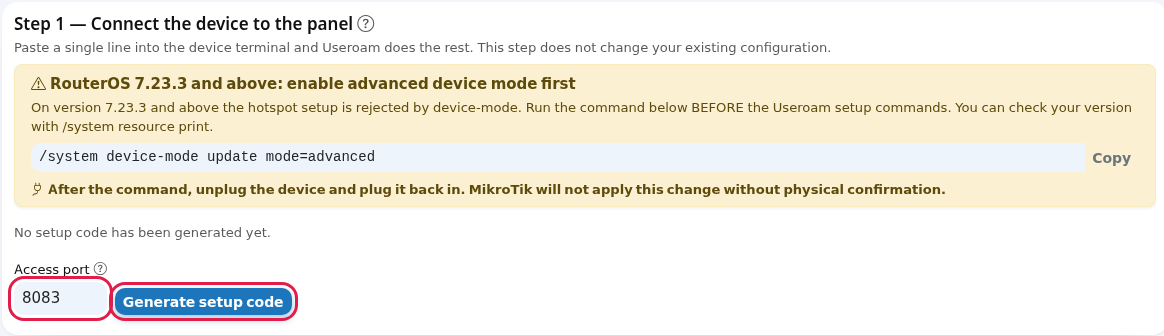
2. **Generate the setup code.** Open **Device Settings** and switch to the **Setup** tab. The **Step 1: Connect the device to the panel** card reads *No setup code has been generated yet.* Check the **Access port** field (it starts with the SSL Port from step 1) and press **Generate setup code**.
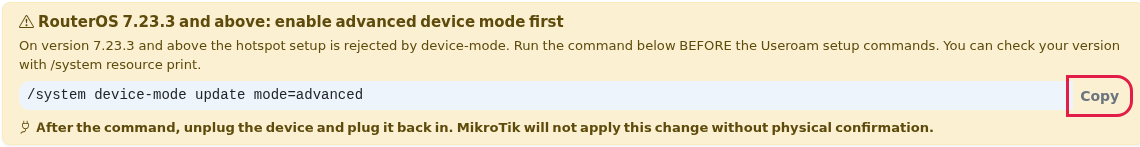
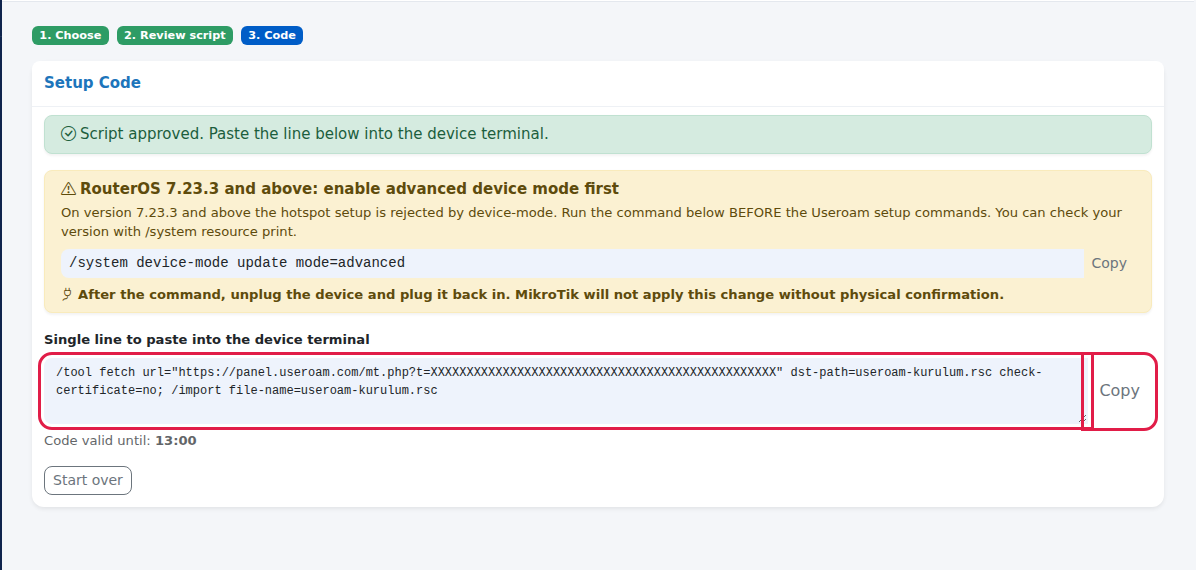
3. **(RouterOS 7.23.3 and above only) Enable device mode.** The yellow box at the top of the card reads *RouterOS 7.23.3 and above: enable advanced device mode first*. Press **Copy**, paste the command into the device terminal and press Enter. Then **unplug the device and plug it back in**; MikroTik will not apply this change without physical confirmation. Skip this step on older versions.
```
/system device-mode update mode=advanced
```
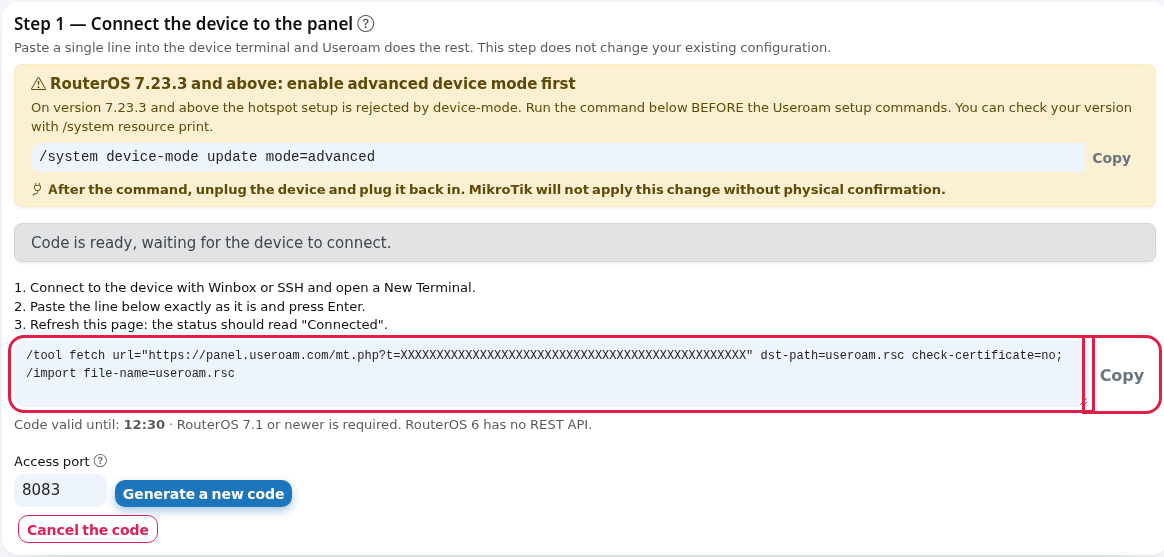
4. **Copy the single line.** Once the code is generated the card reads *Code is ready, waiting for the device to connect.* and shows the command below three short instructions. Press **Copy**. Under the command, **Code valid until** shows the time the code expires; it is valid for 30 minutes and can be used once.
5. **Paste the line into the device terminal.** Connect to the device with Winbox or SSH, open a **New Terminal**, paste the line exactly as it is and press Enter. Lines starting with *Useroam: starting...* scroll by; at the end, inside a frame, you should see *USEROAM: connected. The panel can reach this router. Setup complete.*
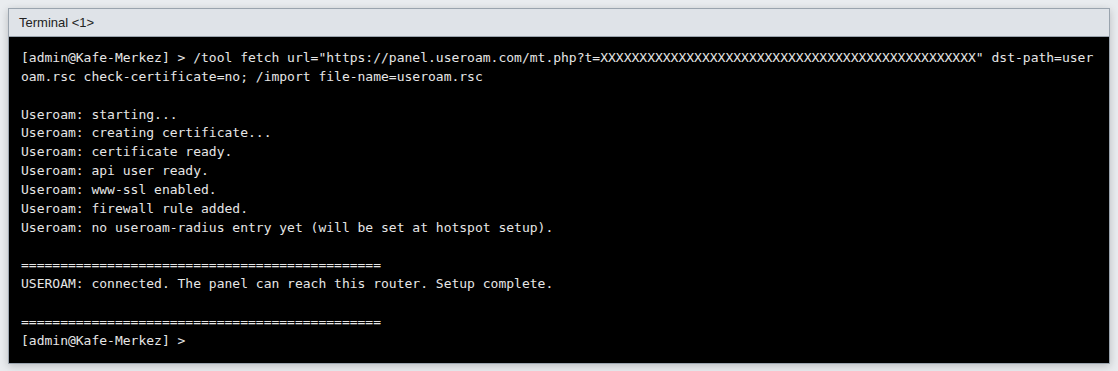
*The image is a sample terminal output; the lines are the setup file's own messages. Depending on your version, RouterOS may print lines of its own as well.*
6. **Refresh the panel.** Reload the **Device Settings** page. The card should read *Connected.* with a **Step 2: Guest network setup** box below it. Press **Open the setup screen**.
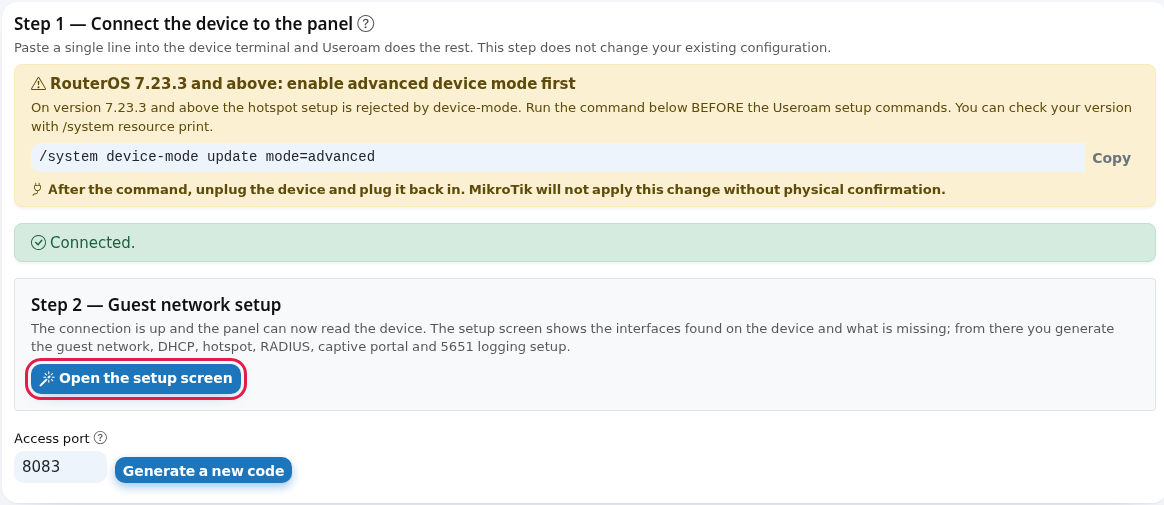
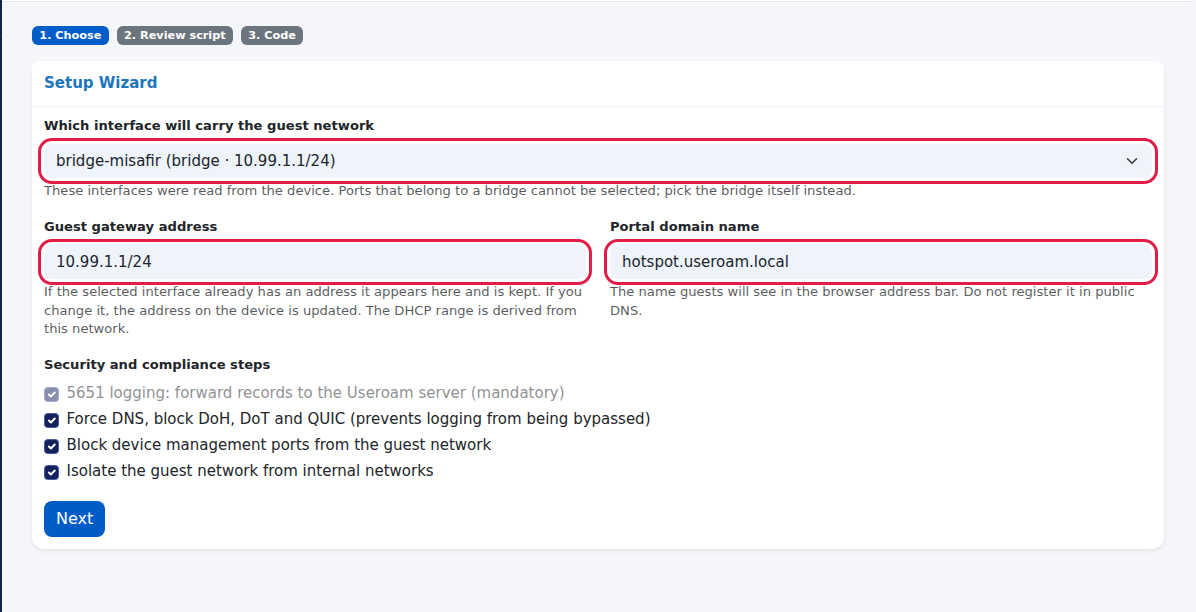
7. **Choose the guest network.** The **Setup** section of the MikroTik Management console opens. The **Current State of the Device** card shows what is present and what is missing. In the **Setup Wizard** card, pick the guest port or bridge from **Which interface will carry the guest network** and check **Guest gateway address** and **Portal domain name**.
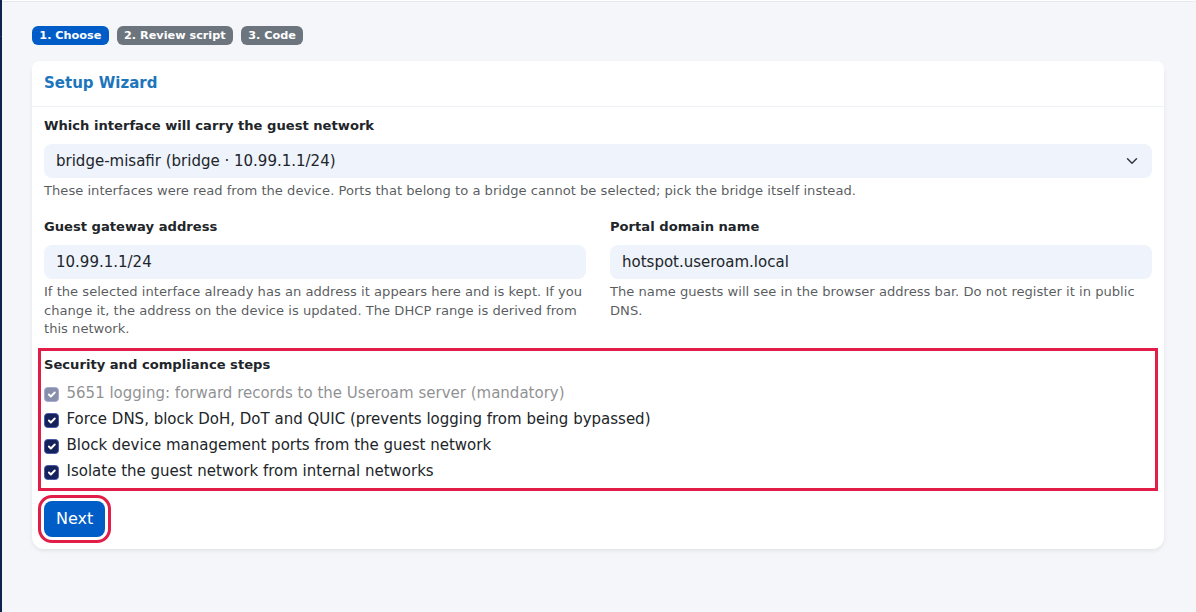
8. **Choose the security steps and press Next.** The boxes under **Security and compliance steps** are ticked by default; 5651 logging is mandatory and cannot be unticked. We recommend leaving them all ticked. Press **Next**.
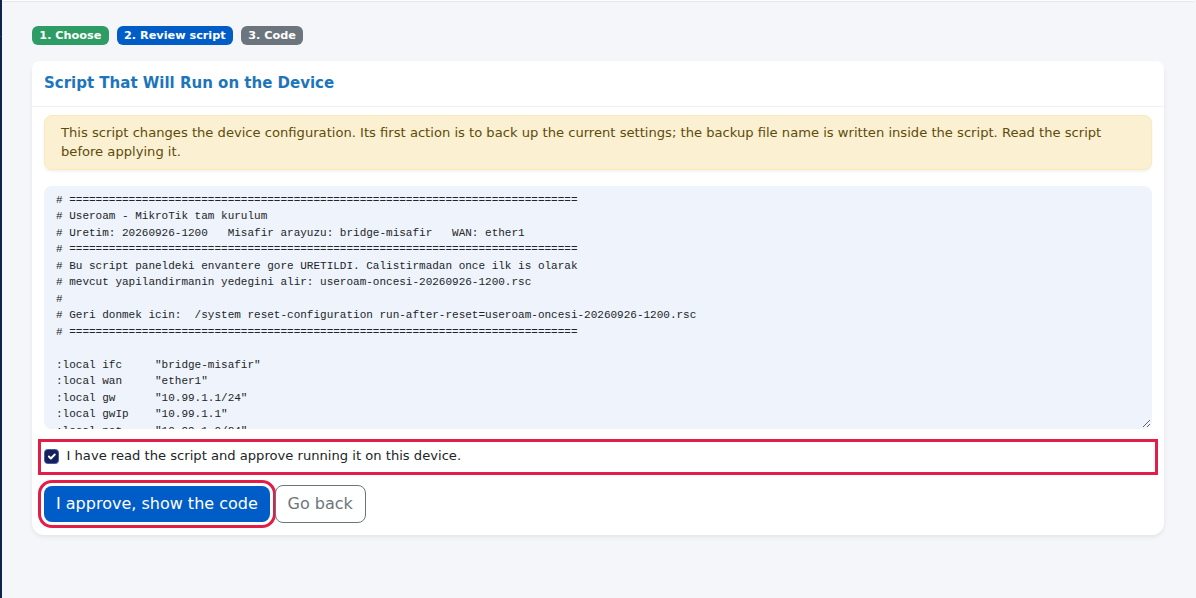
9. **Read and approve the script.** The full setup script that will run on the device is shown. Read it, tick *I have read the script and approve running it on this device.* and press **I approve, show the code**.
10. **Paste the setup line into the device.** The **Single line to paste into the device terminal** appears. Press **Copy**, paste it into the terminal as in step 5 and press Enter. The script first backs up your current settings (*useroam-oncesi-...rsc*), then sets up the guest network.
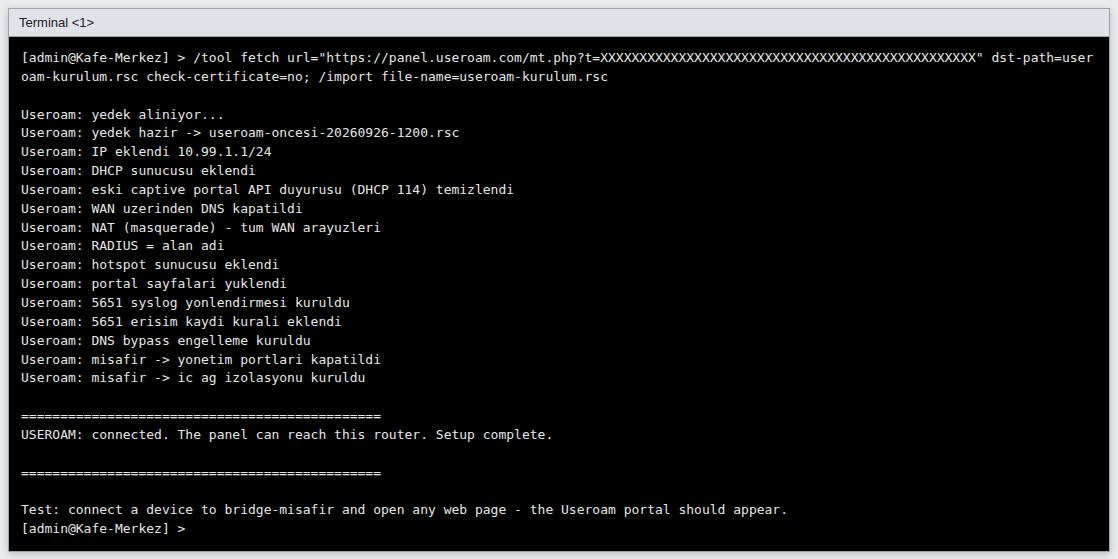
*The image is a sample terminal output; the lines are the script's own messages (some are in Turkish without special characters).*
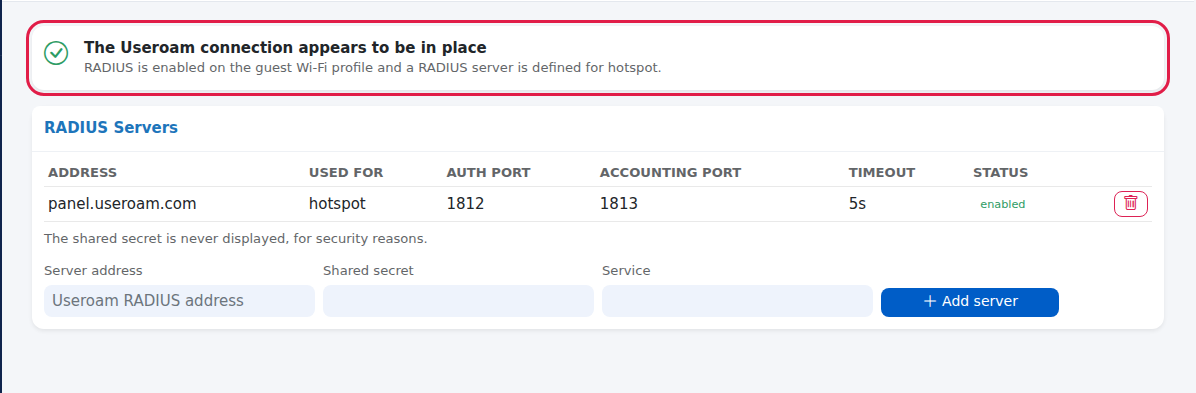
11. **Check the result.** Open the **Useroam Connection** section in the console. At the top it should read *The Useroam connection appears to be in place*. Then connect a phone to the guest network and open any web page: the Useroam welcome page should appear. The guest who logs in shows up in the **Guests Online Now** list of the **Guest Wi-Fi** section.
## Card statuses
What the card says
What it means
What to do
*No setup code has been generated yet.*
No code has been generated for this device.
Press **Generate setup code**.
*Code is ready, waiting for the device to connect.*
A code exists but the device has not fetched it yet.
Paste the line into the device terminal. If the time has passed, press **Generate a new code**.
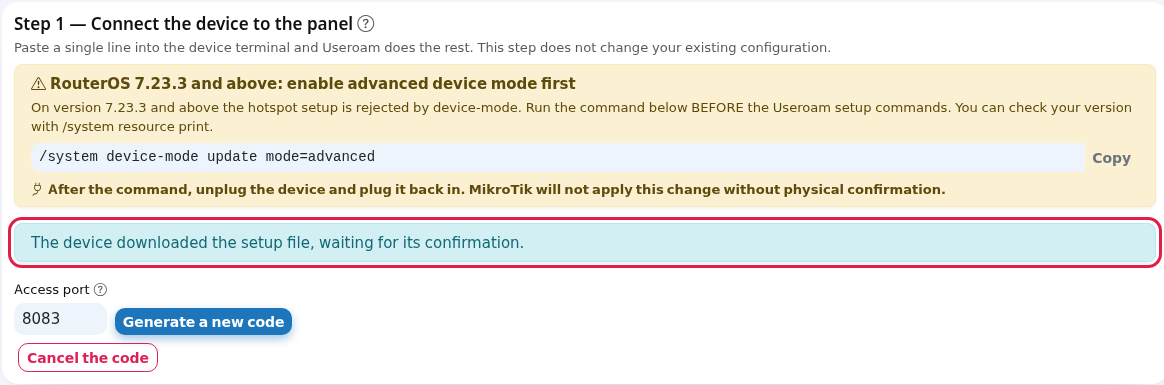
*The device downloaded the setup file, waiting for its confirmation.*
The device downloaded the file but its "ready" message did not arrive.
Check the end of the terminal output (error table below). Wait a moment and reload the page.
*Connected.*
The panel can reach the device.
Press **Open the setup screen** in the Step 2 box.
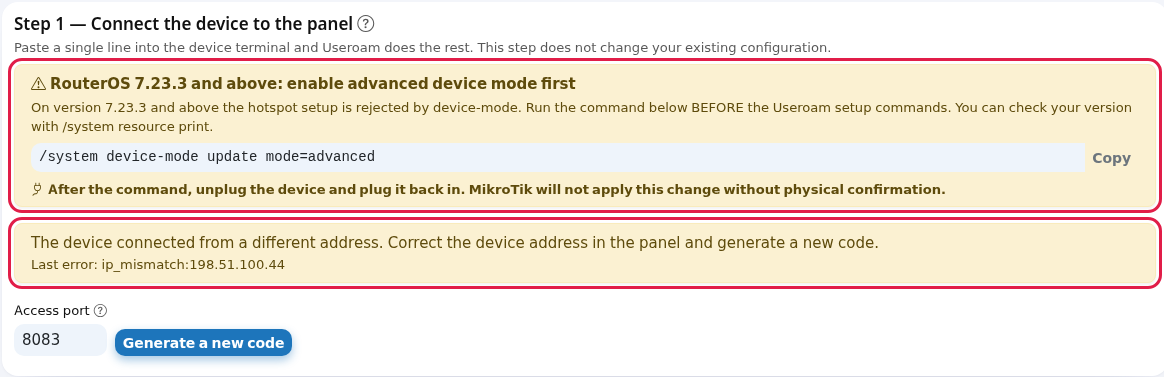
*The device connected from a different address. Correct the device address in the panel and generate a new code.* with **Last error**: *ip\_mismatch:...* below
The device reaches the internet from an address other than the one in the panel. The address in the last error is the device's real outgoing address.
Change the Device Address in **Device Settings** to that address, save, then press **Generate a new code**.
## Card fields and buttons
Field / button
What it does
Example
**Access port**
The port the panel uses to reach the device. 443 for a device facing the internet directly; behind a modem, the external port you forwarded (the forward must target the MikroTik on port 443).
443 or 8443
**Generate setup code** / **Generate a new code**
Generates a new single-use code valid for 30 minutes. A new code invalidates the old one; only one code is valid at a time.
**Copy**
Copies the command line to the clipboard.
**Cancel the code**
Invalidates an unused code. Use it if you shared the code with the wrong person.
**Setup Document**
Opens the MikroTik help (on the English panel it leads to the MikroTik Management book).
**MikroTik Management**
Opens the MikroTik console once the device is connected.
**Legacy setup method (archive)**
The old way for devices set up by uploading hotspot files by hand. Do not use it for new setups.
## What does the single line do on the device?
The line from step 4 (connection setup) only does the following on the device; it does not touch your guest network, bridges, DHCP or existing firewall rules:
1. Version check: stops on RouterOS 6.
2. Creates a certificate for HTTPS management (if missing).
3. Adds a user named *useroam-api* that can only log in from the Useroam panel address (*104.247.174.120*).
4. Enables the device's web service (www-ssl, REST API). If you already have your own certificate, it is kept.
5. Adds a single firewall accept rule for the panel address only (*useroam-api-allow*).
6. If a Useroam RADIUS entry already exists, turns off its Message-Authenticator requirement.
7. Sends a "ready" message to the panel; the panel immediately tries to connect back.
To remove this connection, run these three lines in the terminal:
```
/user remove [find name="useroam-api"]
/user group remove [find name="useroam-api"]
/ip firewall filter remove [find comment="useroam-api-allow"]
```
## Error messages you may see in the terminal
Terminal message
Meaning
What to do
*Setup code is invalid or malformed.*
The code was copied incompletely or damaged.
Copy the line again with **Copy**.
*Setup code is invalid or has already been used.*
The code was not recognised or was already used.
Press **Generate a new code**.
*Setup code was cancelled in the panel. Generate a new one.*
The code was cancelled in the panel or replaced by a newer code.
Use the latest code from the panel.
*Setup code has expired. Generate a new one in the Useroam panel.*
The code expired (connection code 30, setup code 60 minutes).
Generate a new code.
*This device reached us from ... but the panel has ... Fix the device IP in the panel, then retry.*
The device's outgoing address does not match the Device Address in the panel.
Correct the Device Address to the first address, then generate a new code.
*This device is already connected to Useroam.*
The device is already connected.
Nothing to do; go on with **Open the setup screen**.
*Setup code was already used. Generate a new one in the panel.*
The same code was run twice.
Generate a new code.
*USEROAM ERROR: RouterOS 6 detected ...*
The device runs RouterOS 6.
Upgrade to RouterOS 7.1 or newer.
*USEROAM ERROR: certificate signing timed out.*
The device could not create the certificate within 90 seconds.
Run the line again (a new code may be needed).
*USEROAM: device registered, but the panel could NOT connect back.* and *TCP 443 from 104.247.174.120 must reach THIS router.*
The device registered but the panel cannot reach it. Usually the device is behind a modem.
Forward an external port on the modem to port 443 of the MikroTik, enter the external port in **Access port** and generate a new code.
*USEROAM WARNING: could not reach the Useroam panel.*
The device could not reach the panel (no internet or DNS).
Check the device's internet and DNS settings, then run the line again.
*Useroam panel could not read the generated credentials. Generate a new code.* / *Useroam panel database is unavailable, try again later.*
A temporary problem on the panel side.
Generate a new code after a few minutes; contact support if it continues.
## Frequently asked questions
**I pasted the code but the card still says "Code is ready".**
Look at the terminal output. There is usually a message saying the device cannot reach the panel or that the address does not match (table above). If there is no message, reload the page.
**My device is behind a modem. What should I do?**
Forward an external port on the modem (e.g. 8443) to port 443 of the MikroTik. In the panel enter 8443 in **Access port** and press **Generate a new code**. The Device Address in the panel must be the modem's public address.
**Will the single line break my existing settings?**
No. The connection line only adds a certificate, the *useroam-api* user, the web service and one accept rule. The second line, which sets up the guest network, does change settings; this is why the panel first shows you the whole script and why the script takes a backup first. Details are on the [Setup Wizard](/books/mikrotik-management/page/setup-wizard) page.
**I run RouterOS 7.23.3 and the hotspot is not set up.**
Device mode was not enabled, or the device was not unplugged and replugged after the command. Do step 3.
**I shared the code with someone. Is that a problem?**
The code only works for requests from the device address saved in the panel and can be used once. If you are unsure, press **Cancel the code**.
## Related pages
- [Adding a New Device](/books/settings/page/adding-a-new-device)
- [Device Settings](/books/settings/page/device-settings)
- [MikroTik Setup Wizard](/books/mikrotik-management/page/setup-wizard)
- [MikroTik Management](/books/mikrotik-management/page/mikrotik-management)
- [Guest Wi-Fi and Useroam Connection](/books/mikrotik-management/page/guest-wi-fi-and-useroam-connection)
# Setting up MikroTik without exposing it to the internet (offline)
> **There are two setup paths.** In the **automatic setup** ([MikroTik Integration Guide](/books/installation-guides/page/mikrotik-integration-guide)) the Useroam panel connects to your router over the internet. In the **offline setup** (this page) your router is never exposed: the panel asks you two questions, prepares the setup script for your router and gives you a single line to paste into the router's terminal. Both paths set up guest login, Useroam login (RADIUS) and 5651 logging.
## What is it for?
This page explains how to connect your MikroTik router to Useroam without exposing it to the internet, that is, without letting the Useroam panel connect to the router. The panel's **offline setup wizard** does not connect to your router; it asks which interfaces carry the guest network and the internet uplink and builds the setup script from your answers. The router only talks outwards: it downloads the script and the welcome pages from the panel, asks Useroam about guest logins and sends 5651 records to Useroam. No management user, web service or inbound management access is added to your router.
## When to use it
- Your security policy does not allow the router's management service (HTTPS) to be reachable from the internet.
- The router sits behind another modem or a carrier-grade shared IP (CGNAT) and cannot be reached from outside.
- The automatic setup showed *USEROAM: device registered, but the panel could NOT connect back.* and you cannot set up port forwarding (see "If Useroam cannot reach the router" below).
- Your customer's network policy only allows the router to connect outwards and accepts no inbound connections.
## What works with the offline setup?
Feature
Offline setup
Notes
Guest login (SMS, WhatsApp, voucher, hotel and other login methods)
Works
The router asks Useroam over RADIUS. The welcome page is served by Useroam.
Session records (duration, data used)
Works
The router sends session updates every 5 minutes.
**Active Guests** list
Works
The list is built from the session records the router sends. There is no disconnect button in the list.
5651 logging
Works
The router sends its logs to Useroam over UDP 514. **5651 Logging** (5651 Loglama) must be on in the panel.
**Blocked Users**
Works
A blocked guest is rejected at their next login. A session that is already open is not closed.
Group settings (speed, quota, duration, idle time, device count)
Works, applied at login
The settings are sent to the router when the guest logs in. If you change a guest's group later, it takes effect when they log in again. If the group names a router profile or address list, it must exist on the router with the same name (created by hand).
**MikroTik Management** console
Does not work
The console connects to the router over the internet. On an offline router you see the *Cannot reach the device...* warning. Only the **Setup** section opens; that is the offline wizard on this page.
Disconnecting a guest or blocking them on the router instantly from the panel
Does not work
These actions need a connection to the router.
Speed package sales
Not available on MikroTik
Not available with the automatic setup either.
## Before you start
- **RouterOS 7.1 or newer.** You can see your version in the terminal with `/system resource print` (the *version* line).
- **Winbox** and an administrator account on the router. You can download Winbox from the link on the **Setup** tab of **Device Settings**.
- **The public IPv4 address the router uses to reach the internet.** If the router sits behind a modem, this is the modem's public address. It must be entered **exactly** as the **Device Address** in the panel: when the router downloads the setup script, the panel checks which address the request came from and refuses the script if it differs. Useroam also recognises guest logins and 5651 records by this address. If you do not know it, open a "what is my ip" website on a computer in the same network.
- **The router must be able to connect outwards:** HTTPS (TCP 443) to *panel.useroam.com*, UDP 1812 and 1813 for RADIUS, UDP 514 for 5651 records. No port needs to be opened towards the router.
- **Which interface carries the guest network.** The port your guest access point (AP) is plugged into, or the bridge that port belongs to.
## Step by step
1. **(RouterOS 7.23.3 and newer only) Turn on device mode.** In Winbox open **New Terminal**, paste the line below, press Enter, then **unplug the router's power and plug it back in**. On these versions the hotspot cannot be set up until device mode is on. Skip this step on older versions. The panel shows the same warning in a yellow box.
```
/system device-mode update mode=advanced
```
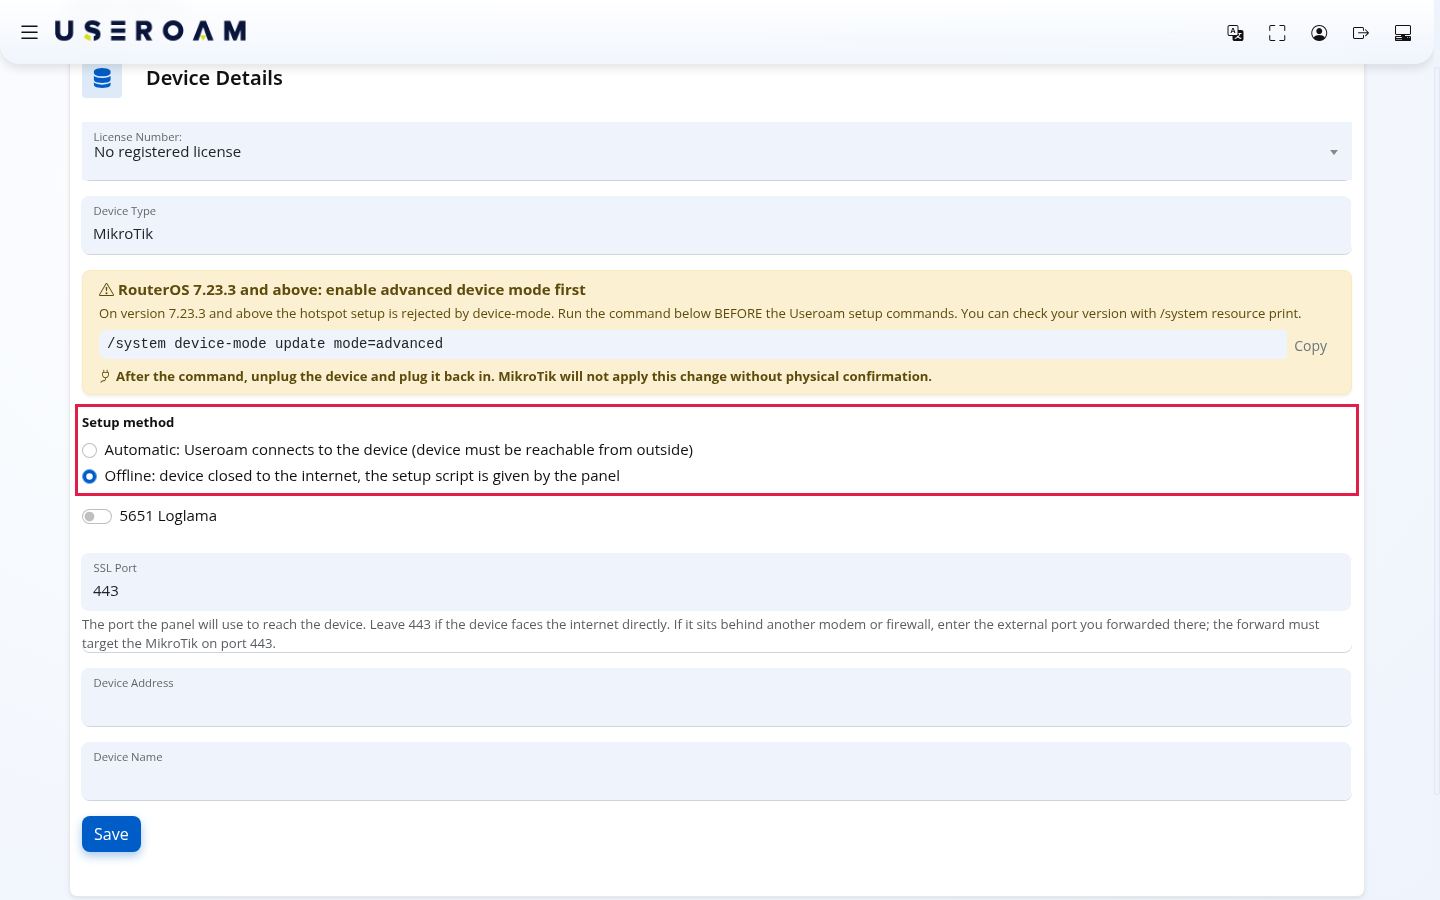
2. **Add the router to the panel and choose Offline.** In **Device Selection** > **New Device**, choose **MikroTik** as the **Device Type**. **Setup method** appears right below it; select **Offline: device closed to the internet, the setup script is given by the panel**. Enter the router's public IPv4 address (for example *203.0.113.10*) as the **Device Address**, turn on **5651 Logging** (on screen: *5651 Loglama*) and press **Save**. The **SSL Port** is not used in the offline setup; it can stay *443*. After saving, the panel takes you straight to the offline setup wizard.
**If the router is already in the panel**, skip this step: open **Device Settings** from the left menu, go to the **Setup** tab and press **Device closed to the internet? Offline setup**. This button also appears on MikroTik routers the panel cannot connect to (no Firewall API connection). The same link is at the top of the **Setup** section in the MikroTik Management console.
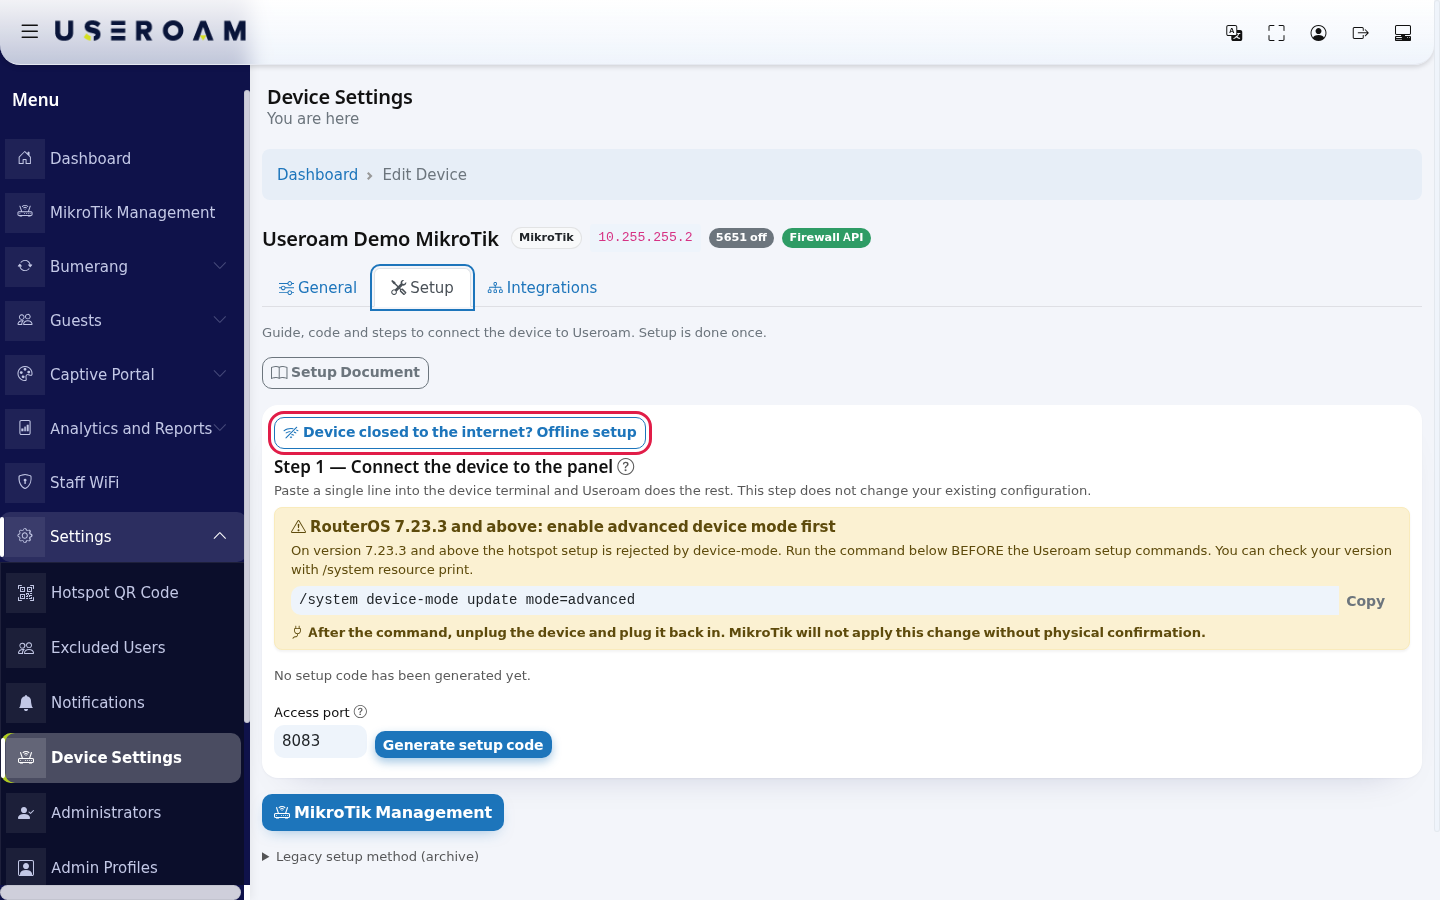
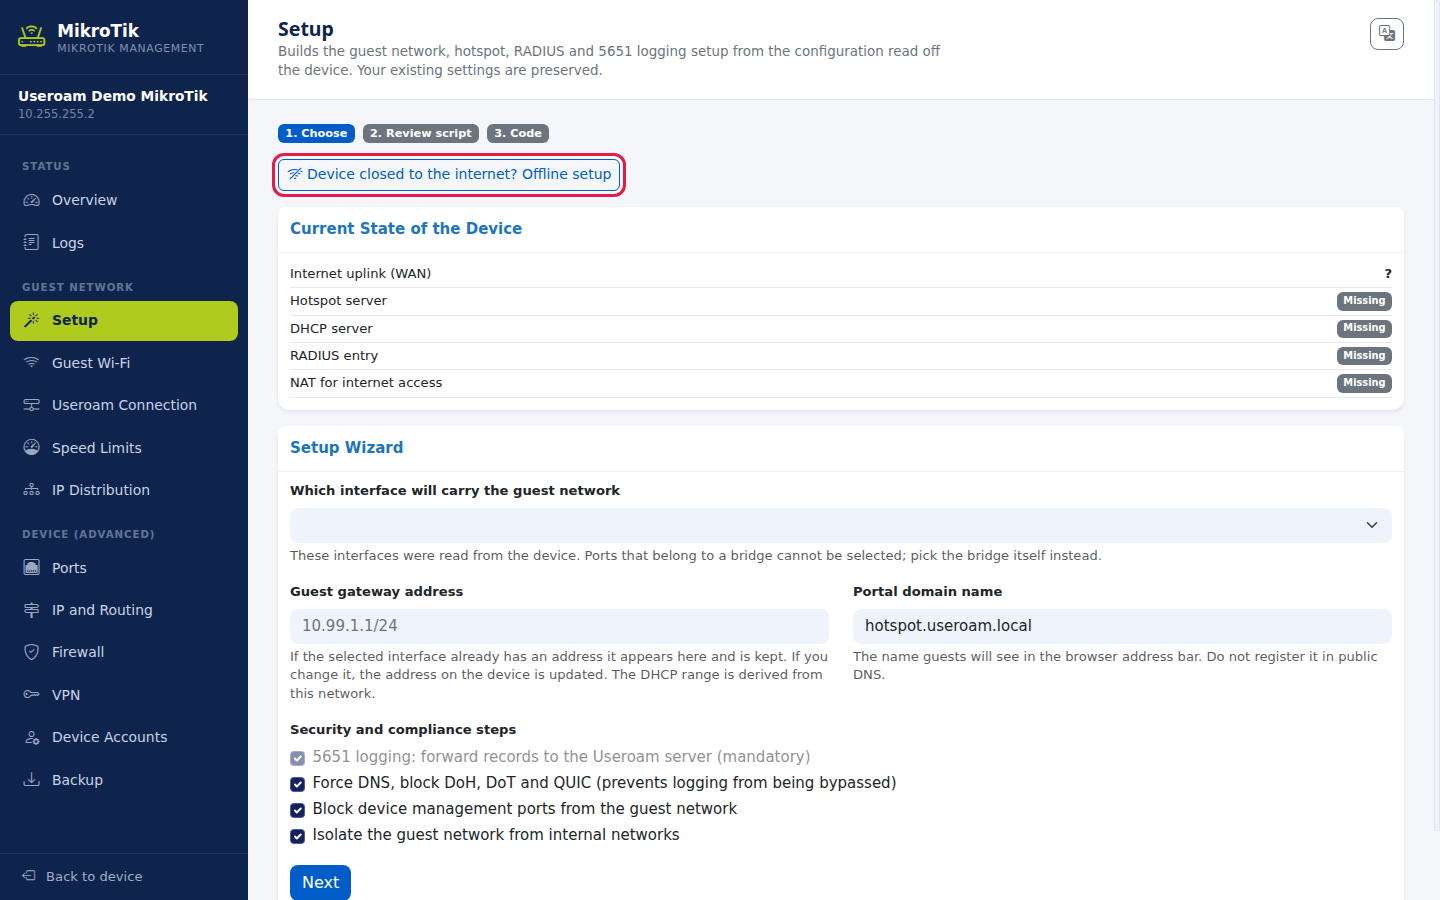
For an offline setup, **do not press** **Generate setup code** on the **Setup** tab. That button is for the automatic setup.
3. **Find the names of the two interfaces.** Type the lines below into the Winbox terminal one by one. They only read; nothing is changed.
```
/interface print
/interface bridge port print
/ip route print where dst-address=0.0.0.0/0
```
- **Internet uplink (WAN):** the interface the active default route leaves through in the output of the third command (for example *ether1* or *pppoe-out1*). In Winbox it is the interface on the *0.0.0.0/0* line under **IP** > **Routes**.
- **Guest interface:** the port or bridge your guest access point is connected to (for example *ether3* or *bridge-misafir*). Do not enter a port that the second command lists as a bridge member; enter the bridge itself. Do not enter the internet interface.
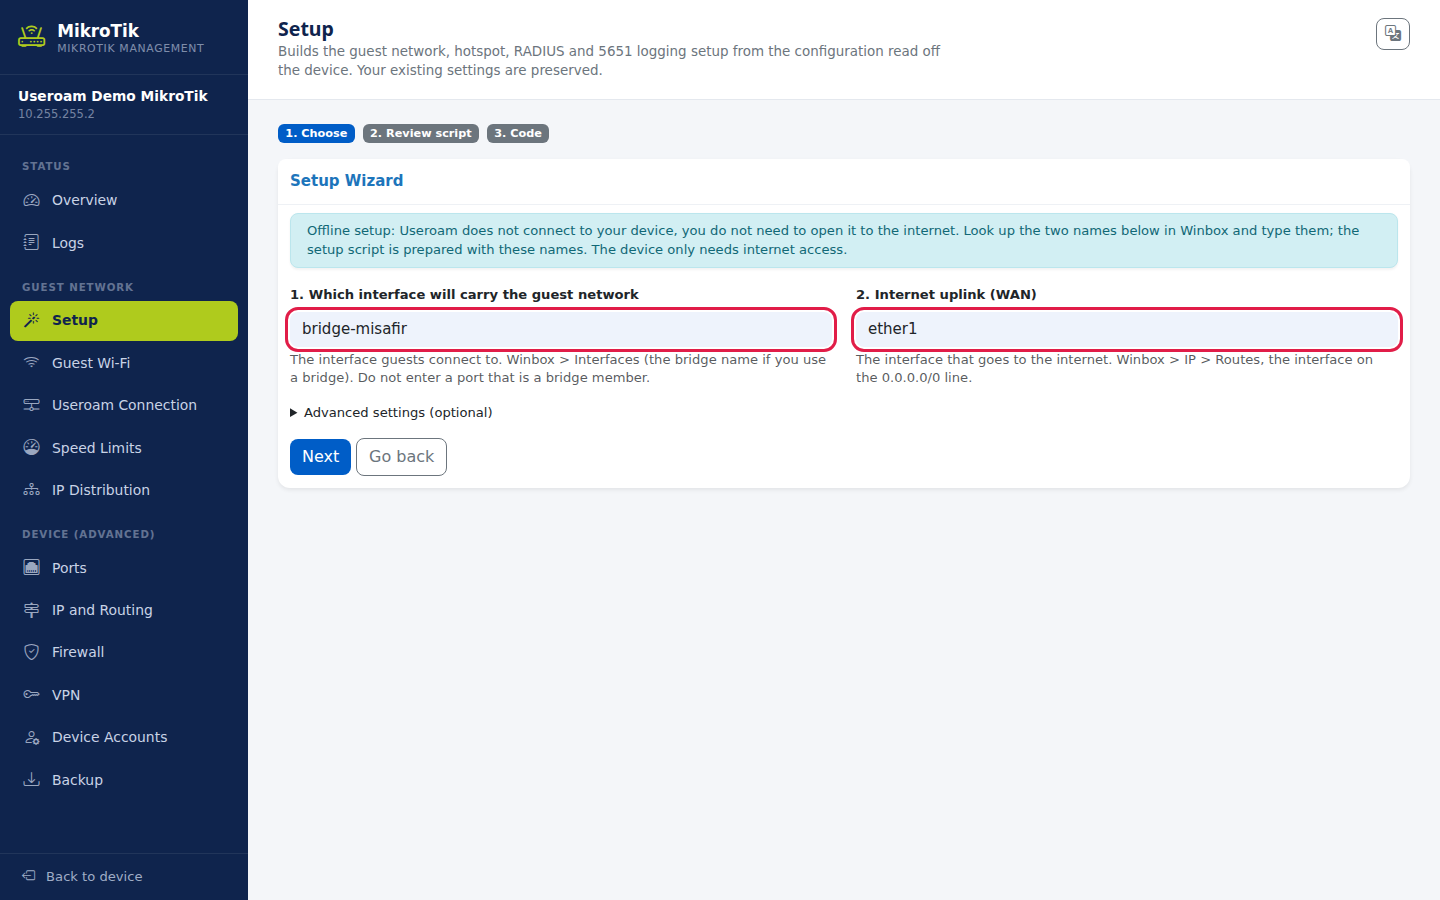
4. **Type the two names into the wizard.** The blue box at the top of the **Setup Wizard** card reads *Offline setup: Useroam does not connect to your device, you do not need to open it to the internet...*. Type the guest interface name (for example *bridge-misafir*) into **1. Which interface will carry the guest network** and the internet interface name (for example *ether1*) into **2. Internet uplink (WAN)**. Type the names exactly as they appear on the router, including upper and lower case.
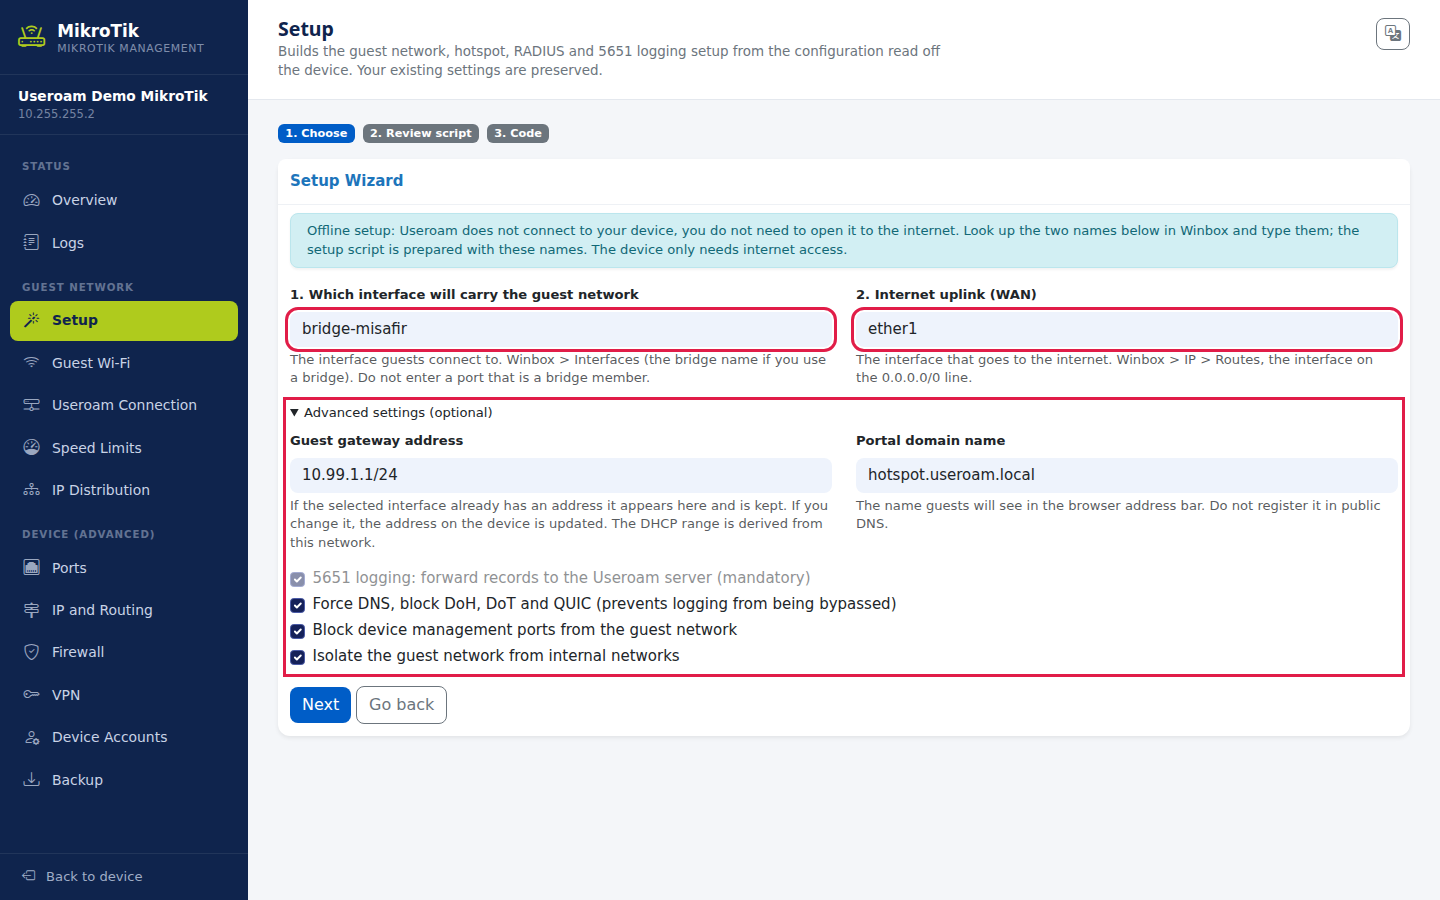
5. **(Optional) Check the advanced settings.** Clicking **Advanced settings (optional)** opens four settings: **Guest gateway address** (default *10.99.1.1/24*), **Portal domain name** (default *hotspot.useroam.local*) and the security boxes. In the offline setup the panel cannot read your router: if the guest interface already has an address you want to keep, enter it here; otherwise the script replaces the interface address with the value in this box. All four security boxes come ticked; the first (5651 logging) cannot be removed, and we recommend leaving the others ticked. If you are unsure, leave this section alone.
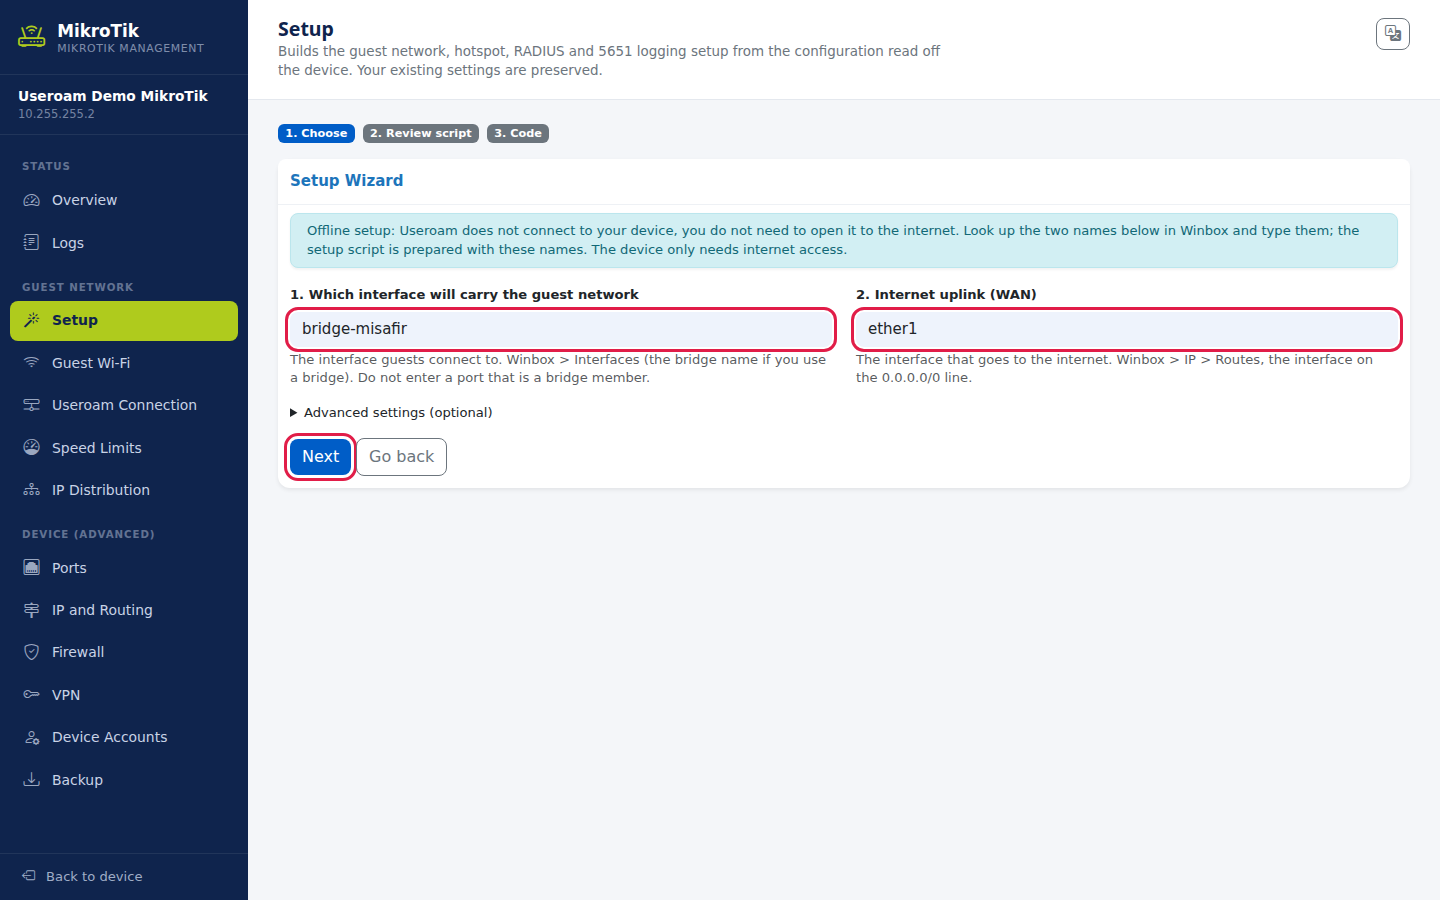
6. **Press Next.** The panel builds the script with the names you typed and prepares a single-use setup code valid for 60 minutes. This button writes nothing to the router. Earlier unused codes for this router become invalid. If a box is empty or a name contains a character that is not allowed (such as a space or a Turkish letter), the browser shows a warning next to the box and the form is not sent. If both names are the same, the red warning *The selected interface was not found on the device. Refresh the page and try again.* appears; type two different names and try again.
7. **Read and approve the script.** In the step badges at the top **2. Review script** turns blue and the **Script That Will Run on the Device** card opens. A plain explanation of what the script does is in the "What does the script do on the device?" table on the [MikroTik Setup Wizard](/books/mikrotik-management/page/setup-wizard) page. After reading it, tick **I have read the script and approve running it on this device.** and press **I approve, show the code**.

8. **Copy the line.** The **Setup Code** card reads *Script approved. Paste the line below into the device terminal.*. Press **Copy** next to the **Single line to paste into the device terminal** box. Apply it before the time shown on the **Code valid until** line.

9. **Paste the line into the router's terminal.** Open **New Terminal** in Winbox, paste the line and press Enter. The router downloads the script from the panel and runs it. First, a backup of your current settings is saved to *useroam-oncesi-<date-time>.rsc*. Then a line starting with *Useroam:* appears for each step; the welcome page files are also downloaded from the panel automatically (*Useroam: portal sayfalari yuklendi*).
At the end you see the lines where the panel tries to connect back to the router. In the offline setup the panel cannot connect to the router, so you may see *USEROAM: device registered, but the panel could NOT connect back.* and lines asking for a port-forward here. **This is expected and not an error**; you do not need a port-forward. The line *USEROAM: setup applied, but the panel could not be notified.* also means the setup was applied.
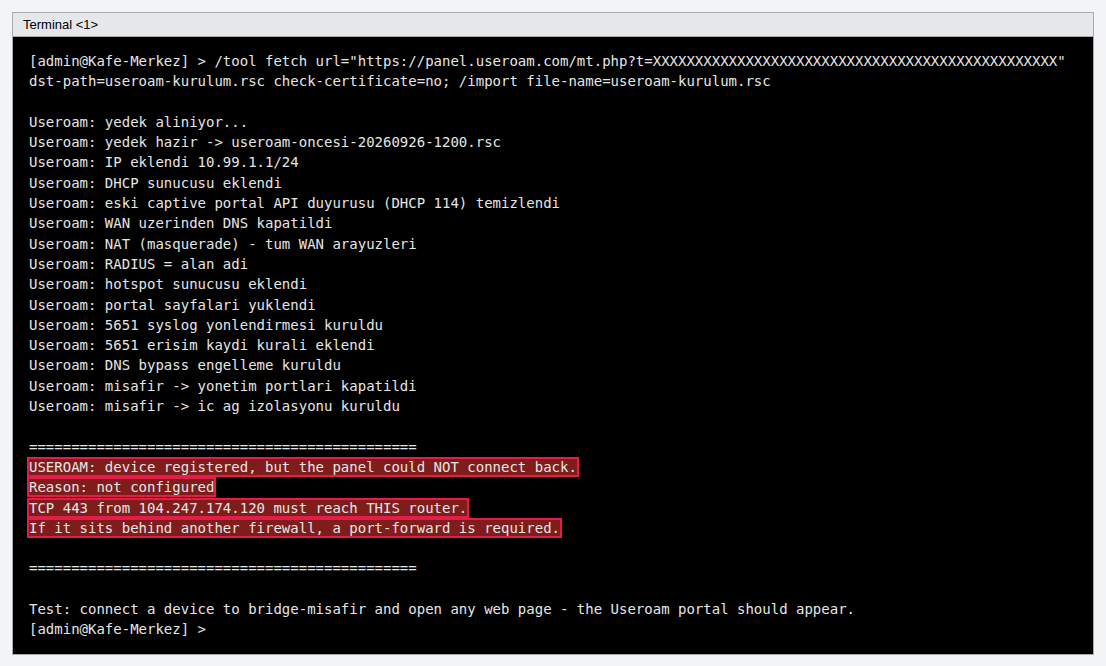
The image is an example terminal output; the lines are the script's own messages. The text on the *Reason* line can differ from router to router. If you see a line starting with *USEROAM WARNING: ... step failed, continuing.*, that step was not applied; note the line and contact our support team.
10. **Check the setup on the router.** The commands below only read. Look for the values on the right in each output:
`/system logging action print where name=useroamremote`
*remote=104.247.174.120*, *remote-port=514*
`/ip firewall filter print where comment~"useroam"`
The *useroam-5651-log* rule at the top of the list
11. **Try a guest login and confirm it in the panel.** Connect a phone to the guest Wi-Fi and open a web page: the Useroam welcome page should open. Log in. Then in the panel:
- The phone's session should appear in **Guests** > **Active Guests** ([Active Guests](/books/guests/page/active-guests)).
- A record for this router should appear in **Analytics and Reports** > **5651 Logs** ([5651 Logs](/books/analytics-and-reports/page/5651-logs)).
## Fields and buttons in the offline wizard
Field / button
What it does
Example
**Setup method** (New Device, only when MikroTik is selected)
**Automatic: Useroam connects to the device (device must be reachable from outside)** or **Offline: device closed to the internet, the setup script is given by the panel**. With Offline, the offline wizard opens right after saving; with Automatic you return to Device Settings.
Offline
**Device closed to the internet? Offline setup**
On the Setup tab of Device Settings and at the top of MikroTik Management > Setup. Opens the offline wizard.
**1. Which interface will carry the guest network**
The router's name for the interface guests connect to. Below it: *The interface guests connect to. Winbox > Interfaces (the bridge name if you use a bridge). Do not enter a port that is a bridge member.* Up to 32 characters; letters, digits, dot, hyphen and underscore.
bridge-misafir
**2. Internet uplink (WAN)**
The name of the interface that goes to the internet. Below it: *The interface that goes to the internet. Winbox > IP > Routes, the interface on the 0.0.0.0/0 line.* It cannot be the same as the guest interface.
ether1
**Advanced settings (optional)**
Opens the gateway, portal domain name and security boxes.
**Guest gateway address**
The guest network's address on the router and its size. The IP range handed to guests is derived from it. The script replaces or adds the address on the guest interface with this value.
10.99.1.1/24
**Portal domain name**
The name guests see in the browser address bar. Do not register it in public DNS.
hotspot.useroam.local
**5651 logging: forward records to the Useroam server (mandatory)**
Always on, cannot be removed.
ticked
**Force DNS, block DoH, DoT and QUIC (prevents logging from being bypassed)**
Forces guests' DNS queries through the router.
ticked
**Block device management ports from the guest network**
Stops guests from reaching the router's SSH, Telnet, Winbox and API ports.
ticked
**Isolate the guest network from internal networks**
Stops guests from reaching internal networks such as office, till or cameras.
ticked
**Next**
Builds the script and moves to step 2 (Review script). Writes nothing to the router.
**Go back**
Returns to the automatic setup wizard.
The screens of steps 2 and 3 (Review script, Setup Code) are the same as in the automatic setup: [MikroTik Setup Wizard](/books/mikrotik-management/page/setup-wizard).
## Errors you may see in the terminal
If the panel does not accept the code, the router downloads a short error file instead of the script and the terminal shows this frame: *USEROAM: kurulum kodu kabul edilmedi* (setup code not accepted), with a *Sebep:* (reason) line below it. No setting is changed.
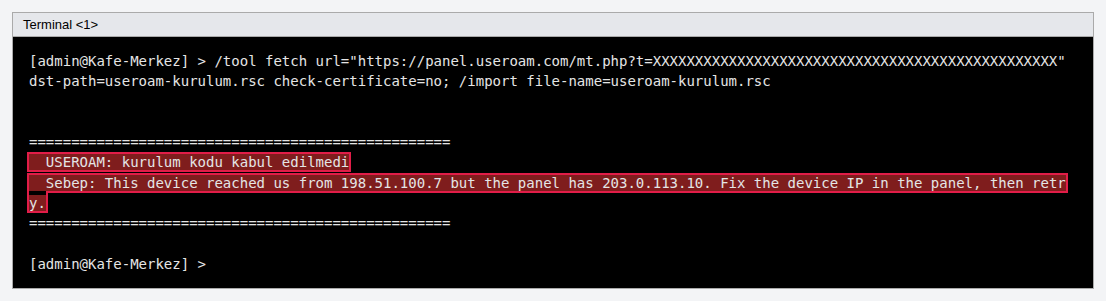
Reason line
What it means
What to do
*This device reached us from 198.51.100.7 but the panel has 203.0.113.10. Fix the device IP in the panel, then retry.*
The router reached the panel from a public address different from the **Device Address** in the panel. The first address is the one the router really uses.
In **Device Settings** > **General**, correct the **Device Address** to the first address in the message and save. The code has not been used, so if it has not expired you can paste the same line again; if unsure, generate a new code in the wizard.
*Setup code has expired. Generate a new one in the Useroam panel.*
The code is older than 60 minutes.
Run the wizard again and generate a new code.
*Setup code was already used. Generate a new one in the panel.*
The code is single-use; this line was already run.
Generate a new code if you want to set up again.
*Setup code was cancelled in the panel. Generate a new one.*
A newer script was generated for the same router after this code; the old code was cancelled.
Use the line you generated last.
*Setup code is invalid or has already been used.* or *Setup code is invalid or malformed.*
The line was copied incompletely or wrongly.
Copy the line again with the **Copy** button in the panel.
*This device is already connected to Useroam.*
The setup with this code is already complete.
Nothing to do.
*Useroam panel database is unavailable, try again later.*
The panel could not answer for a moment.
Try the same line again in a few minutes.
If the terminal shows an error from the */tool fetch* command itself instead of the Useroam frame (the download does not finish), the router cannot reach *panel.useroam.com* over HTTPS. Check the router's DNS settings and any rule that blocks outbound traffic; if the problem continues, use the manual setup below.
## If the wizard cannot be used: manual setup
The normal path is the wizard above. The manual setup below is only for cases where you cannot use the wizard: for example, the router cannot reach *panel.useroam.com* over HTTPS (the setup line cannot download the script), or you cannot generate a router-specific line in the panel. On this path you write the Device Password and the interface names into the file yourself and upload the welcome page files yourself. Do not apply both paths to the same router.
1. **(RouterOS 7.23.3 and newer only) Turn on device mode.** In Winbox open **New Terminal**, paste the line below, press Enter, then **unplug the router's power and plug it back in**. On these versions the hotspot cannot be set up until device mode is on. Skip this step on older versions.
```
/system device-mode update mode=advanced
```
2. **Add the router to the panel.** In **Device Selection** > **New Device**, choose **MikroTik** as the device type. Enter the router's public IPv4 address (for example *203.0.113.10*) as the device address, turn on **5651 Logging** and press **Save**. The SSL port is not used in the offline setup; it can stay at *443*. Skip this step if the router is already added.

**Do not press** **Generate setup code** on the **Setup** tab for an offline setup. That button is for the automatic setup; if you press it, the panel starts waiting to connect to the router.
3. **Copy the Device Password.** Open **Device Settings** from the left menu. On the **General** tab, under **Device connection**, copy the **Device Password**. You will put it into the setup file in step 7. Do not change it.
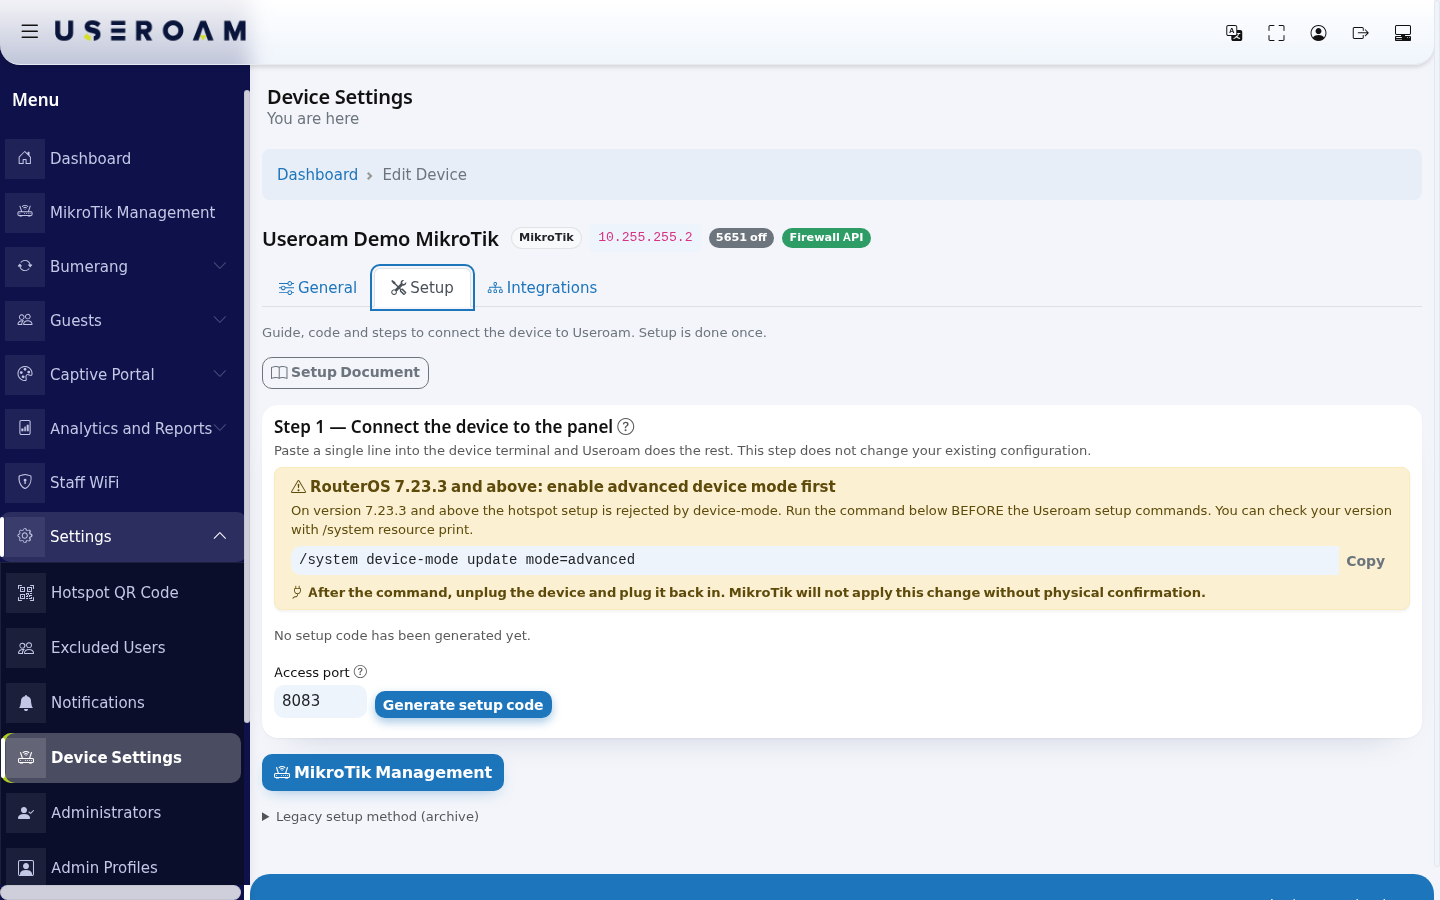
4. **Download the welcome page files.** Switch to the **Setup** tab. At the bottom, open **Legacy setup method (archive)** and press **Download hotspot files**. In the *Your Files Are Ready* window press **Download**. A ZIP file is saved to your computer; the welcome pages inside it are specific to this router.
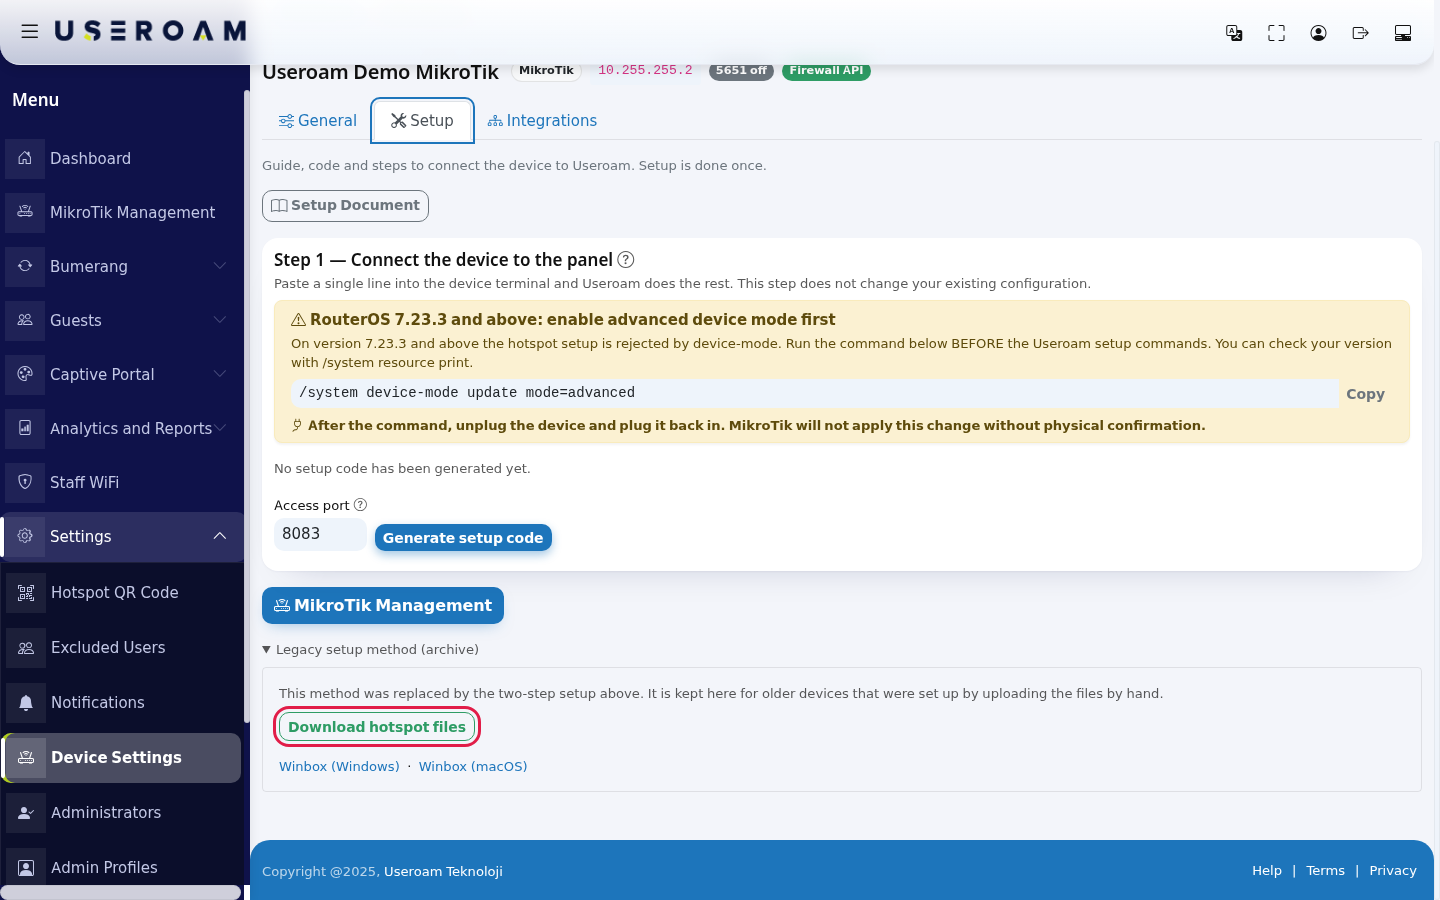
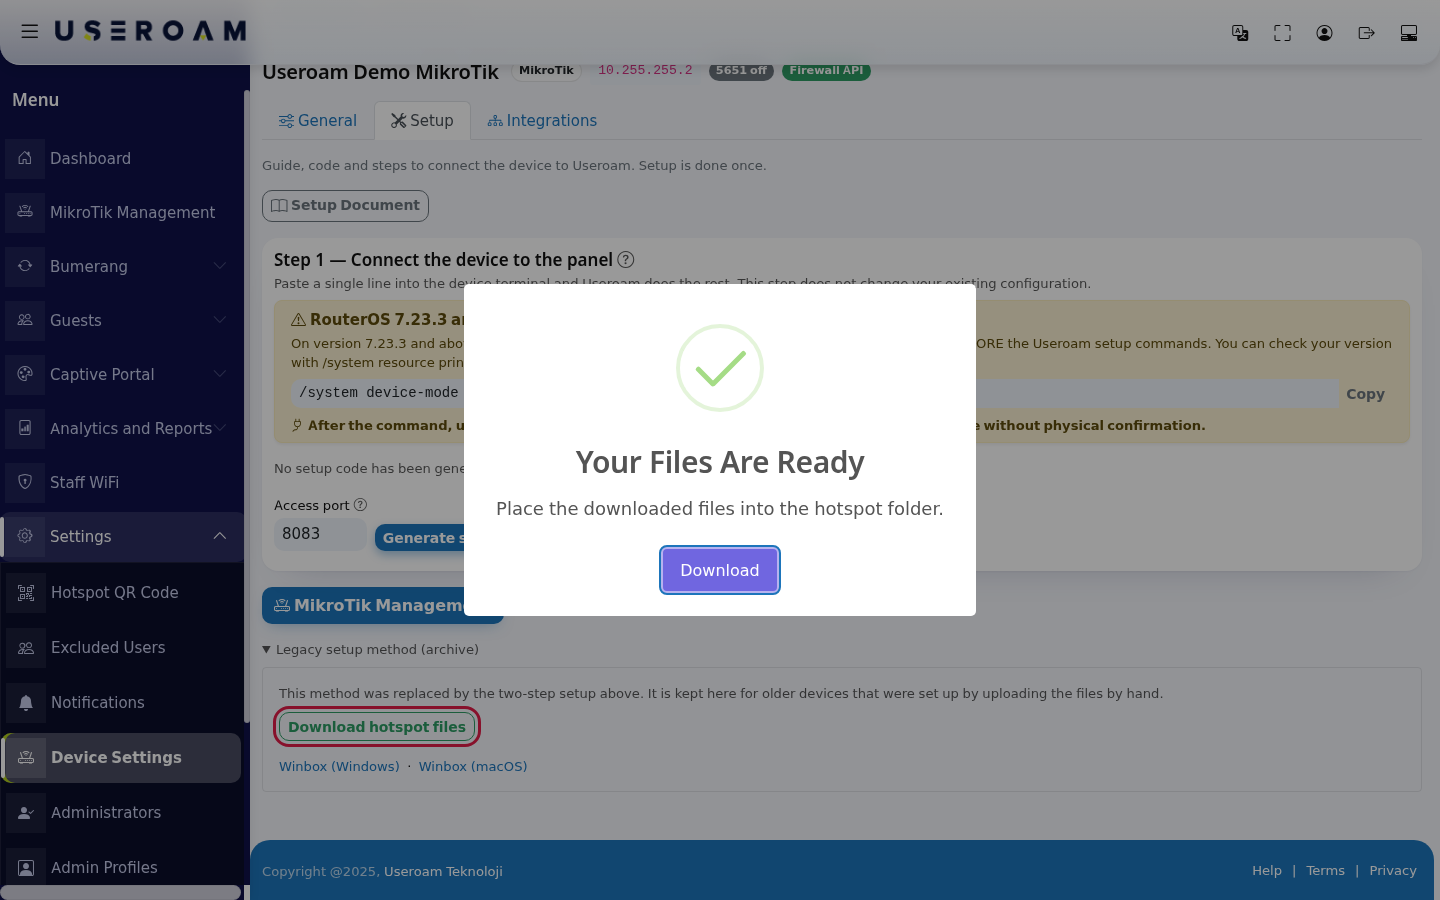
Extract the ZIP into a folder. **Do not use** the *useroam-init.rsc* file inside it: it is an old setup file, it does not set up 5651 logging and it contains settings that stop the login screen from opening on phones. The setup file on this page replaces it. You only need these 8 files from the ZIP: *login.html, status.html, logout.html, error.html, rlogin.html, redirect.html, alogin.html, md5.js*.
5. **Read the router's ports.** Type the lines below into the terminal one by one. They only read; nothing is changed.
```
/interface print
/interface bridge port print
/ip route print where dst-address=0.0.0.0/0
/ip address print
```
- **Internet port (WAN):** in the output of the third command, the interface the active default route goes out of (for example *ether1* or *pppoe-out1*). This name will be *<WAN\_ARAYUZU>*.
- **Guest port:** the port or bridge the guest access point is connected to (for example *ether3* or *bridge-guest*). This name will be *<MISAFIR\_ARAYUZU>*. Do not pick a port that the second command lists as a member of a bridge; pick the bridge itself. Do not pick the internet port.
6. **Check for an earlier setup on the router.** These commands also only read.
```
/ip hotspot print
/radius print
/ip dhcp-server print
/system logging action print
```
The setup file treats existing settings like this:
If the router already has
What the setup file does
An IP address on the guest port
**Replaces** it with *10.99.1.1/24*. To keep your address, write it in step 7.
A DHCP server on the guest port
Keeps it and does not add a new one.
A hotspot on the guest port
Does not add another hotspot; links the existing one to the Useroam profile.
RADIUS, NAT or pre-login allow entries that Useroam added earlier
Deletes and re-adds them. Your other RADIUS entries are not touched.
A hotspot or RADIUS setup from another company
Leaves it alone; both setups stay side by side and may clash. Contact our support team first.
Do not apply both the automatic setup and the offline setup to the same router. If the router was already set up automatically, you do not need this page.
7. **Prepare the setup file.** Open the **Setup file** box below, copy all of its content and paste it into Notepad. Replace the three values at the top with your own; keep the quotation marks, remove the angle brackets (< >):
In the file
Replace with
From
Example
*<MISAFIR\_ARAYUZU>*
Name of the guest port
Step 5
bridge-guest
*<WAN\_ARAYUZU>*
Name of the internet port
Step 5
ether1
*<CIHAZ\_SIFRESI>*
Device Password
Step 3
After the change the lines look like this:
```
:local ifc "bridge-guest"
:local wan "ether1"
:local rsecret "Your-Device-Password"
```
The guest network comes as *10.99.1.0/24*. If this network is already used elsewhere on your router, change the *gw*, *gwIp*, *net* and *havuz* lines in the same pattern; otherwise leave them. Save the file as *useroam-offline.rsc* (in Notepad set **Save as type** to **All Files** so *.txt* is not added). The comments inside the file are in Turkish; they do not change how it works.
**Setup file** (press to open)
```
# =============================================================================
# Useroam - MikroTik internete acmadan (offline) kurulum
# Kaynak: panelin kurulum sihirbazinin urettigi script;
# panel baglantisi gerektiren iki bolum cikarildi (portal dosyalari, panele bildirim).
# Duzenlenecek 3 deger:
# 10.99.1.1/24 cihazda baska bir agda kullaniliyorsa gw/gwIp/net/havuz satirlarini degistirin.
#
# Ilk is mevcut yapilandirmanin yedegini alir: useroam-oncesi-manuel.rsc
# Geri donmek icin: /system reset-configuration run-after-reset=useroam-oncesi-manuel.rsc
# =============================================================================
:local ifc ""
:local wan ""
:local gw "10.99.1.1/24"
:local gwIp "10.99.1.1"
:local net "10.99.1.0/24"
:local havuz "10.99.1.10-10.99.1.254"
:local dom "hotspot.useroam.local"
:local rsecret ""
:local panelIp "104.247.174.120"
:put ""
:put "Useroam: yedek aliniyor..."
/export file=("useroam-oncesi-manuel")
:delay 3s
:put "Useroam: yedek hazir -> useroam-oncesi-manuel.rsc"
# --- 1) Misafir agi IP adresi -----------------------------------------------
# Arayuzde adres varsa DEGISTIRILIR (yukaridaki gw degeri), yoksa eklenir.
/ip address
:local mevcutAdr [find interface=$ifc]
:if ([:len $mevcutAdr] = 0) do={
add address=$gw interface=$ifc comment="useroam-gw"
:put "Useroam: IP eklendi $gw"
} else={
set [:pick $mevcutAdr 0] address=$gw
:put "Useroam: IP guncellendi $gw"
}
# --- 2) DHCP havuzu + sunucusu ----------------------------------------------
/ip pool
:if ([:len [find name="useroam-pool"]] = 0) do={
add name=useroam-pool ranges=$havuz
} else={ set [find name="useroam-pool"] ranges=$havuz }
/ip dhcp-server
:if ([:len [find interface=$ifc]] = 0) do={
add name=useroam-dhcp interface=$ifc address-pool=useroam-pool lease-time=1h disabled=no
:put "Useroam: DHCP sunucusu eklendi"
} else={ :put "Useroam: mevcut DHCP sunucusu korundu" }
/ip dhcp-server network
:if ([:len [find address=$net]] = 0) do={
add address=$net gateway=$gwIp dns-server=$gwIp comment="useroam"
}
# --- 2b) Eski captive portal API duyurusu (DHCP 114) TEMIZLENIR -------------
# CAPPORT_114_KALDIR_2026: duyurulan capport API'si "captive" degerini dogru
# soyleyemedigi surece iOS'un kendi probe'undan (captive.apple.com) KOTUDUR:
# iOS API'ye guvenir ve giris basarili olsa bile "Done" dugmesini hic gostermez
# (sahada olculdu, kaldirilinca duzeldi). Bu yuzden artik TANIMLANMIYOR ve
# eski kurulumlardan kalan kayit VARSA SILINIYOR.
# Yalnizca KENDI kaydimiz hedeflenir (useroam-capport / -set); musterinin
# kendi DHCP secenegine ve option-set'ine DOKUNULMAZ.
# Sira zorunlu: once ag baglantisi cozulur, sonra set, sonra option
# (kullanimdayken silinmez; yarim kalirsa ag kaydinda dangling referans kalir).
:do {
:foreach n in=[/ip dhcp-server network find] do={
:if ([/ip dhcp-server network get $n dhcp-option-set] = "useroam-capport-set") do={
/ip dhcp-server network set $n dhcp-option-set=""
}
}
/ip dhcp-server option sets remove [/ip dhcp-server option sets find name="useroam-capport-set"]
/ip dhcp-server option remove [/ip dhcp-server option find name="useroam-capport"]
:put "Useroam: eski captive portal API duyurusu (DHCP 114) temizlendi"
} on-error={ :put "Useroam: DHCP 114 temizligi atlandi (menu yok veya kayit yok)" }
# --- 3) DNS (misafirlerin cozumleme yapabilmesi + 5651 gorunurlugu) ---------
/ip dns
set allow-remote-requests=yes
:if ([:len [get servers]] = 0) do={ set servers=8.8.8.8,1.1.1.1 }
# Misafirlere DNS acmak, cihazi INTERNETE de acik cozumleyici yapar (amplification).
# WAN uzerinden gelen DNS sorgulari kapatilir.
/ip firewall filter
:if ([:len [find comment="useroam-dns-wan-drop"]] = 0) do={
add chain=input in-interface=$wan protocol=udp dst-port=53 action=drop comment="useroam-dns-wan-drop"
add chain=input in-interface=$wan protocol=tcp dst-port=53 action=drop comment="useroam-dns-wan-drop"
:put "Useroam: WAN uzerinden DNS kapatildi"
}
# --- 4) Internet cikisi (NAT) -----------------------------------------------
# COKLU_WAN_NAT_2026: tek arayuze baglamak, ikinci/yedek WAN devreye girdiginde misafirin
# internetini kesiyordu. Artik WAN arayuz LISTESI kullaniliyor: kac hat olursa olsun calisir.
# Liste yoksa olusturulur, secilen WAN uye degilse eklenir (musteri sonradan hat eklerse
# yalnizca listeye uye yapmasi yeter).
:do {
:if ([:len [/interface list find name="WAN"]] = 0) do={
/interface list add name=WAN comment="useroam"
}
:if ([:len [/interface list member find list=WAN interface=$wan]] = 0) do={
/interface list member add list=WAN interface=$wan comment="useroam"
}
# Eski tek-arayuzlu kural varsa yenisiyle degistirilir.
:foreach r in=[/ip firewall nat find comment="useroam-masq"] do={ /ip firewall nat remove $r }
/ip firewall nat add chain=srcnat action=masquerade src-address=$net out-interface-list=WAN comment="useroam-masq"
:put "Useroam: NAT (masquerade) - tum WAN arayuzleri"
} on-error={ :put "USEROAM WARNING: NAT step failed, continuing." }
# --- 5) RADIUS --------------------------------------------------------------
# Once alan adi denenir (IP degisirse cihaz dokunmadan calismaya devam eder),
# kabul edilmezse IP'ye dusulur.
/radius
:foreach r in=[find comment="useroam-radius"] do={ remove $r }
:do {
add address=panel.useroam.com secret=$rsecret service=hotspot timeout=5s comment="useroam-radius"
:put "Useroam: RADIUS = alan adi"
} on-error={
add address=$panelIp secret=$rsecret service=hotspot timeout=5s comment="useroam-radius"
:put "Useroam: RADIUS = IP (alan adi kabul edilmedi)"
}
# RouterOS 7.2x: cevapta Message-Authenticator zorunlulugunu kapat (otomatik baglanti kurulumu ile ayni).
# Bu ayar olmayan eski surumlerde satir atlanir.
:do {
/radius set [find comment="useroam-radius"] require-message-auth=no
:put "Useroam: radius message-auth requirement disabled."
} on-error={ :put "Useroam: require-message-auth bu surumde yok, atlandi." }
# --- 6) Hotspot profili + sunucusu ------------------------------------------
/ip hotspot profile
:if ([:len [find name="useroam-profile"]] = 0) do={
add name=useroam-profile hotspot-address=$gwIp dns-name=$dom html-directory=hotspot \
login-by="http-chap,http-pap" use-radius=yes radius-interim-update=5m \
nas-port-type=wireless-802.11 split-user-domain=no
} else={
set [find name="useroam-profile"] hotspot-address=$gwIp dns-name=$dom html-directory=hotspot \
login-by="http-chap,http-pap" use-radius=yes
}
/ip hotspot
:if ([:len [find interface=$ifc]] = 0) do={
add name=useroam-hotspot interface=$ifc address-pool=useroam-pool profile=useroam-profile \
addresses-per-mac=2 idle-timeout=30m keepalive-timeout=2m disabled=no
:put "Useroam: hotspot sunucusu eklendi"
} else={
set [find interface=$ifc] profile=useroam-profile disabled=no
:put "Useroam: mevcut hotspot sunucusu Useroam profiline baglandi"
}
# --- 7) Captive portal sayfalari --------------------------------------------
# OFFLINE: dosyalar panelden indirilip Winbox Files ile hotspot klasorune elle yuklenir.
# --- 8) Walled garden (giris oncesi erisilmesi gerekenler) ------------------
# Isletim sisteminin BAGLANTI KONTROLU adresleri (captive.apple.com,
# connectivitycheck.*, msftconnecttest) BILEREK YOK: izin verilirse cihaz "internet
# var" sanar ve captive giris ekrani (iOS CNA) hic acilmaz.
# WG_CNA_2026: joker Google izinleri (*.google.com, *.gstatic.com) KALDIRILDI.
# Sebep: Android baglanti kontrolu connectivitycheck.gstatic.com ve
# connectivitycheck.google.com uzerinden yapiliyor. Joker izinli oldugunda cihaz
# "internet var" sanip GIRIS EKRANINI HIC ACMIYOR (sessiz ariza; E40'ta ayni hatayi
# Apple alan adlari icin yasamistik). Google ile giris icin gereken adresler tek tek yazildi.
/ip hotspot walled-garden
:foreach w in=[find comment="useroam-wg"] do={ remove $w }
:foreach d in={
"*.useroam.com"; "useroam.com"; "panel.useroam.com"; "cloud.useroam.com";
"*.wa.me"; "*.whatsapp.com"; "*.whatsapp.net"; "g.whatsapp.net"; "mmg.whatsapp.net"; "*.fbsbx.com";
"*.facebook.com"; "*.fbcdn.net";
"accounts.google.com"; "accounts.youtube.com"; "apis.google.com"; "ssl.gstatic.com";
"fonts.gstatic.com"; "*.googleapis.com"; "*.recaptcha.net";
"appleid.apple.com";
} do={ add dst-host=$d comment="useroam-wg" }
/ip hotspot walled-garden ip
:foreach w in=[find comment="useroam-wg"] do={ remove $w }
add dst-address=$panelIp action=accept comment="useroam-wg"
add dst-address=157.240.0.0/16 action=accept comment="useroam-wg"
add dst-address=31.13.0.0/16 action=accept comment="useroam-wg"
# --- 9) 5651 loglama: syslog -> Useroam ------------------------------------
:do {
:if ([:len [/system logging action find name="useroamremote"]] = 0) do={
/system logging action add name=useroamremote target=remote remote=$panelIp remote-port=514
} else={
/system logging action set [/system logging action find name="useroamremote"] remote=$panelIp remote-port=514
}
:foreach t in={"hotspot";"dhcp";"firewall";"hotspot,account"} do={
:if ([:len [/system logging find topics=$t action="useroamremote"]] = 0) do={
/system logging add topics=$t action=useroamremote
}
}
:put "Useroam: 5651 syslog yonlendirmesi kuruldu"
} on-error={ :put "USEROAM WARNING: syslog step failed, continuing." }
# --- 9b) 5651 ERISIM KAYDI: her yeni misafir baglantisi loglanir ------------
# Sophos'ta firewall connection log'unun karsiligi. MikroTik "firewall" topic'i
# ancak bir kuralda log=yes/action=log varsa konusur; bu kural onu tetikler.
# action=log SONLANDIRICI DEGIL -> trafigi etkilemez, sadece kayit uretir.
# Kural listenin BASINA alinir, yoksa musterinin mevcut drop kurallari golgeler.
:do {
:if ([:len [/ip firewall filter find comment="useroam-5651-log"]] = 0) do={
/ip firewall filter add chain=forward src-address=$net connection-state=new action=log log-prefix="useroam5651" comment="useroam-5651-log"
}
:do {
/ip firewall filter move [/ip firewall filter find comment="useroam-5651-log"] destination=0
} on-error={ :put "USEROAM WARNING: 5651 log kurali basa TASINAMADI - kural listenin sonunda. Mevcut drop kurallariniz onu golgeleyebilir, kayit uretmeyebilir." }
:put "Useroam: 5651 erisim kaydi kurali eklendi"
} on-error={ :put "USEROAM WARNING: 5651 access-log step failed, continuing." }
# --- 10) DNS bypass engelleme (DoH / DoT / QUIC) ---------------------------
:do {
:if ([:len [/ip firewall nat find comment="useroam-dns-udp"]] = 0) do={
/ip firewall nat add chain=dstnat src-address=$net protocol=udp dst-port=53 action=redirect to-ports=53 comment="useroam-dns-udp"
}
:if ([:len [/ip firewall nat find comment="useroam-dns-tcp"]] = 0) do={
/ip firewall nat add chain=dstnat src-address=$net protocol=tcp dst-port=53 action=redirect to-ports=53 comment="useroam-dns-tcp"
}
:if ([:len [/ip firewall filter find comment="useroam-dot-tcp"]] = 0) do={
/ip firewall filter add chain=forward src-address=$net protocol=tcp dst-port=853 action=drop comment="useroam-dot-tcp"
}
:if ([:len [/ip firewall filter find comment="useroam-dot-udp"]] = 0) do={
/ip firewall filter add chain=forward src-address=$net protocol=udp dst-port=853 action=drop comment="useroam-dot-udp"
}
:if ([:len [/ip firewall filter find comment="useroam-quic"]] = 0) do={
/ip firewall filter add chain=forward src-address=$net protocol=udp dst-port=443 action=drop comment="useroam-quic"
}
:put "Useroam: DNS bypass engelleme kuruldu"
} on-error={ :put "USEROAM WARNING: dns-hardening step failed, continuing." }
# --- 11) Misafir -> cihaz yonetimi kapali ----------------------------------
# 80/443 KASITLI OLARAK ACIK: captive portal sayfasi bu portlardan servis edilir.
:do {
:if ([:len [/ip firewall filter find comment="useroam-mgmt-drop"]] = 0) do={
/ip firewall filter add chain=input src-address=$net protocol=tcp dst-port=22,23,8291,8728,8729 action=drop comment="useroam-mgmt-drop" place-before=0
}
:put "Useroam: misafir -> yonetim portlari kapatildi"
} on-error={ :put "USEROAM WARNING: mgmt-drop step failed, continuing." }
# --- 12) Misafir -> ic aglar izolasyonu ------------------------------------
# Cihazin ic aglarini VARSAYMAK yerine ozel adres uzayinin tamami kapatilir.
# Misafir-misafir izolasyonu da bunun yan urunu olarak gelir.
:do {
:if ([:len [/ip firewall filter find comment="useroam-izole"]] = 0) do={
/ip firewall filter add chain=forward src-address=$net dst-address=10.0.0.0/8 action=drop comment="useroam-izole"
/ip firewall filter add chain=forward src-address=$net dst-address=172.16.0.0/12 action=drop comment="useroam-izole"
/ip firewall filter add chain=forward src-address=$net dst-address=192.168.0.0/16 action=drop comment="useroam-izole"
}
:put "Useroam: misafir -> ic ag izolasyonu kuruldu"
} on-error={ :put "USEROAM WARNING: isolation step failed, continuing." }
# --- Bitti ------------------------------------------------------------------
:put ""
:put "Useroam: kurulum komutlari tamamlandi."
:put "Simdi portal dosyalarini (login.html vb.) hotspot klasorune yukleyin."
:put "Test: connect a device to $ifc and open any web page - the Useroam portal should appear."
:put ""
```
8. **Upload the file to the router.** In Winbox open **Files** from the left menu and drag *useroam-offline.rsc* into the window. Check: the command below should list the file.
```
/file print where name~"useroam-offline"
```
9. **Run the setup file.** Type this into the terminal and press Enter:
```
/import file-name=useroam-offline.rsc
```
Lines starting with *Useroam:* scroll by. First, a backup of your current settings is written to *useroam-oncesi-manuel.rsc*. At the end you should see *Useroam: kurulum komutlari tamamlandi.* ("setup commands finished"). A line starting with *USEROAM WARNING: ... step failed, continuing.* means that step was not applied; note the line and contact our support team. The line *Useroam: require-message-auth bu surumde yok, atlandi.* ("not available in this version, skipped") is not an error.
10. **Upload the welcome page files.** The hotspot folder is created by the setup. In Winbox **Files**, open the *hotspot* folder and drag the 8 files from step 4 into it. Confirm overwriting files with the same name. To see the folder name:
```
/ip hotspot profile print where name=useroam-profile
```
The output shows *html-directory=hotspot*. Check:
```
/file print where name~"hotspot/login.html"
```
11. **Check the setup on the router.** The commands below only read. Look for the values on the right in each output:
`/system logging action print where name=useroamremote`
*remote=104.247.174.120*, *remote-port=514*
`/ip firewall filter print where comment~"useroam"`
The *useroam-5651-log* rule at the top of the list
`/ip firewall nat print where comment="useroam-masq"`
A masquerade rule for the guest network
12. **Test a guest login and check the panel.** Connect a phone to the guest Wi-Fi and open any web page: the Useroam welcome page should appear. Log in. Then in the panel:
- In **Guests** > **Active Guests** the phone's session should be listed ([Active Guests](/books/guests/page/active-guests)).
- In **Analytics and Reports** > **5651 Logs** a record should appear for this router ([5651 Logs](/books/analytics-and-reports/page/5651-logs)).
### How does the manual setup file differ from the wizard?
The file is the same script the wizard generates; a plain explanation of each step is in the "What does the script do on the device?" table on the [MikroTik Setup Wizard](/books/mikrotik-management/page/setup-wizard) page. Differences in the offline version:
- It does not download the welcome page files from the panel; you upload them in step 10.
- It does not notify the panel when it finishes.
- It does not turn on the setting that listens for RADIUS requests from outside (disconnect requests). Useroam does not send such requests today.
- It turns off a RADIUS setting that, on RouterOS 7.2x, sends guests back to the welcome page after login (*require-message-auth=no*).
- All four security steps are on (5651 logging, DNS/DoT/QUIC blocking, closing management ports to guests, isolating guests from internal networks).
## How do I go back?
The script first backs up your current settings: *useroam-oncesi-<date-time>.rsc* with the wizard (the file name is shown in the terminal on the *Useroam: yedek hazir ->* line), *useroam-oncesi-manuel.rsc* with the manual setup. If you run the manual setup file a second time, this backup is overwritten with the settings at that moment (already set up); download the first backup from **Files** to your computer before the second run. To go back completely, use the backup file name:
```
/system reset-configuration run-after-reset=useroam-oncesi-manuel.rsc
```
This command **resets** the router and reloads the backup; your connection drops meanwhile. This way back has not been tested by Useroam. Use it only when you are at the router and sure; if unsure, contact our support team.
## If Useroam cannot reach the router (automatic setup)
In the automatic setup the panel connects over HTTPS to the router's device address and **Access port** (RouterOS *www-ssl* service, REST API). If the connection is not made within 4 seconds, the router counts as unreachable. If the terminal shows *USEROAM: device registered, but the panel could NOT connect back.* or the console shows *Cannot reach the device. It must run RouterOS 7.1 or newer and have the web service (www-ssl) enabled.*, check the following in order:
Possible cause
How to check
Fix
RouterOS 6
*version* in `/system resource print` starts with 6.
Upgrade to RouterOS 7.1 or newer, or use the offline setup. RouterOS 6 has no REST API.
Web service off
In `/ip service print where name=www-ssl` the service is disabled (marked *X*) or has no certificate.
Run the automatic setup line again; it turns the service and certificate on.
Web service limited to other addresses
In the same output the *address* field is filled and does not include *104.247.174.120*.
Add this address to the allowed addresses.
Router behind a modem
In `/ip address print` the internet port's address starts with 10.x, 172.16-31.x or 192.168.x.
On the modem forward an external port (for example 8443) to port 443 of the MikroTik, enter that port as **Access port** in the panel and generate a new code.
Carrier shared IP (CGNAT)
The internet port's address is between 100.64 and 100.127, or the address the router sees differs from the public address in the panel.
It cannot be reached from outside. Use the offline setup, or ask your provider for a static (public) IP.
A firewall or the internet provider blocks 443
Is there a `/ip firewall filter print where comment="useroam-api-allow"` rule at the top of the list; is incoming 443 blocked on the modem or by the provider.
If the rule is missing, run the setup line again. If the provider blocks it, use another external port.
The Useroam user was changed
`/user print where name~"useroam"` shows *address=104.247.174.120/32* and group *useroam-api*.
Run the setup line again (generate a new code).
The router's certificate changed
You reset the router or changed the *www-ssl* certificate. If the panel stored the certificate fingerprint, it will not connect with a different certificate.
Contact our support team.
**When should I switch to the offline setup?** When the router is behind CGNAT, when you cannot set up port forwarding, or when you do not want the router's management service exposed to the internet. With the offline setup, the features marked "Does not work" in the table above are not available.
**Does a VPN give the panel access back?** No. [VPN (WireGuard) Setup](/books/mikrotik-management/page/vpn-wireguard-setup) is for you and your staff to reach the business's internal network from outside. The Useroam panel does not connect to the router through the VPN, and the VPN wizard itself needs the panel to reach the router.
## Frequently asked questions
**Does the offline setup open any port to the router from outside?**
The script adds no management user, web service or inbound management access, and it blocks DNS queries arriving from the internet side. The wizard script turns on the setting that accepts disconnect requests from the RADIUS server (*/radius incoming*, UDP 3799). The manual setup file does not turn it on.
**The terminal said "could NOT connect back". Did the setup fail?**
No. In the offline setup the panel does not connect to the router, so this line is expected. Check the result with the commands in step 10 and by trying a guest login with a phone.
**It says "kurulum kodu kabul edilmedi" and "reached us from".**
The **Device Address** in the panel is not the address the router uses to reach the internet. Save the first address in the message as the **Device Address** in **Device Settings** > **General** and run the line again. If this address stays wrong, guest login and 5651 logging do not work either.
**The code expired or I used it twice.**
The code is valid for 60 minutes and can be used once. Run the wizard again and generate a new code.
**The welcome page does not open.**
Check with `/file print where name~"hotspot/"` that the welcome files were downloaded; if the terminal showed lines like *Useroam: login.html indirilemedi* (could not be downloaded), run the script again. Make sure the device address in the panel is the router's real public address. On RouterOS 7.23.3 and newer, if you did not turn on device mode the hotspot may not have been created (`/ip hotspot print` is empty).
**Login works but the guest falls back to the welcome page.**
On RouterOS 7.2x the *require-message-auth* setting of the RADIUS entry can cause this. If `/radius print detail` does not show *require-message-auth=no* on the Useroam entry, run: `:do { /radius set [find comment="useroam-radius"] require-message-auth=no } on-error={}`. The manual setup file sets this itself.
**There are no records in 5651 Logs.**
Check that **5651 Logging** is on in the panel, that the device address is the router's public address, and that the router can send UDP 514 outwards. Records are matched by the router's public address.
**Can I switch to the automatic setup later?**
Yes. The single line in the [MikroTik Integration Guide](/books/installation-guides/page/mikrotik-integration-guide) only opens the panel connection on the router; the guest network was built with the same names, so you do not need to set it up again.
**I ran useroam-init.rsc. What should I do?**
Contact our support team. That file makes an old setup (it allows the phones' connectivity-check addresses and does not set up 5651 logging).
## Related pages
- [MikroTik Integration Guide](/books/installation-guides/page/mikrotik-integration-guide) (automatic setup)
- [MikroTik Setup Wizard](/books/mikrotik-management/page/setup-wizard)
- [Adding a New Device](/books/settings/page/adding-a-new-device)
- [Device Settings](/books/settings/page/device-settings)
- [Groups](/books/guests/page/groups)
- [5651 Logs](/books/analytics-and-reports/page/5651-logs)
# Ruijie Integration Guide
This guide walks you through the complete integration between a **Ruijie / Reyee gateway** and Useroam Cloud — captive portal authentication (WiFiDog external portal) and legal 5651 syslog forwarding.
> **Before you start:** you need administrator access to the Ruijie web interface, the gateway's active WAN IP address, and the hardware serial number printed on the device label.
---
### **1 - Adding the device to the Useroam panel**
First, sign in to your panel at **[panel.useroam.com](https://panel.useroam.com)** and add a **New Device**.
- **Device Type:** select **Ruijie**.
- **5651 Logging:** tick the 5651 Logging checkbox.
- **Device Serial Number:** \[CRITICAL STEP\] enter the original hardware serial number in full, exactly as printed on the label underneath the device or as shown in the web interface. The Ruijie integration will not work reliably unless this serial number is correct.
- **Device Address:** enter the active WAN IP address the gateway uses to reach the internet.
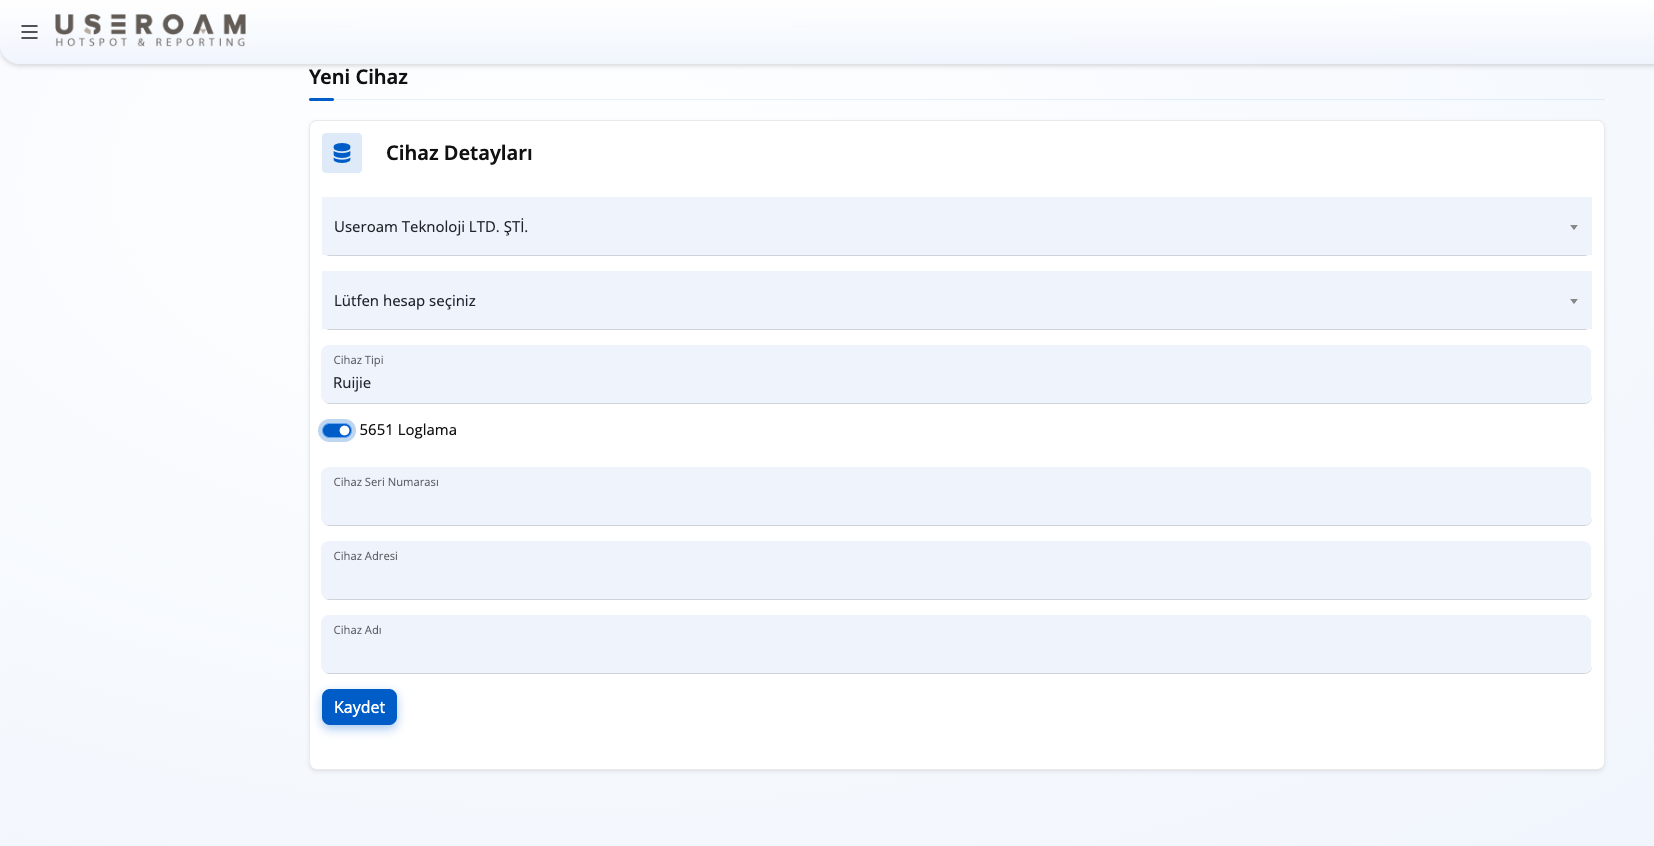
---
### **2 - Allowlist settings for trusted IPs (Allowlist → Dest. IP)**
In the Ruijie management interface, go to **Object > User Authentication > Authentication Settings** from the top menu. Under the **Allowlist** tab, select the **Dest. IP** option and allow the Useroam Cloud server IP address (`104.247.174.120`) together with your hotspot service networks.
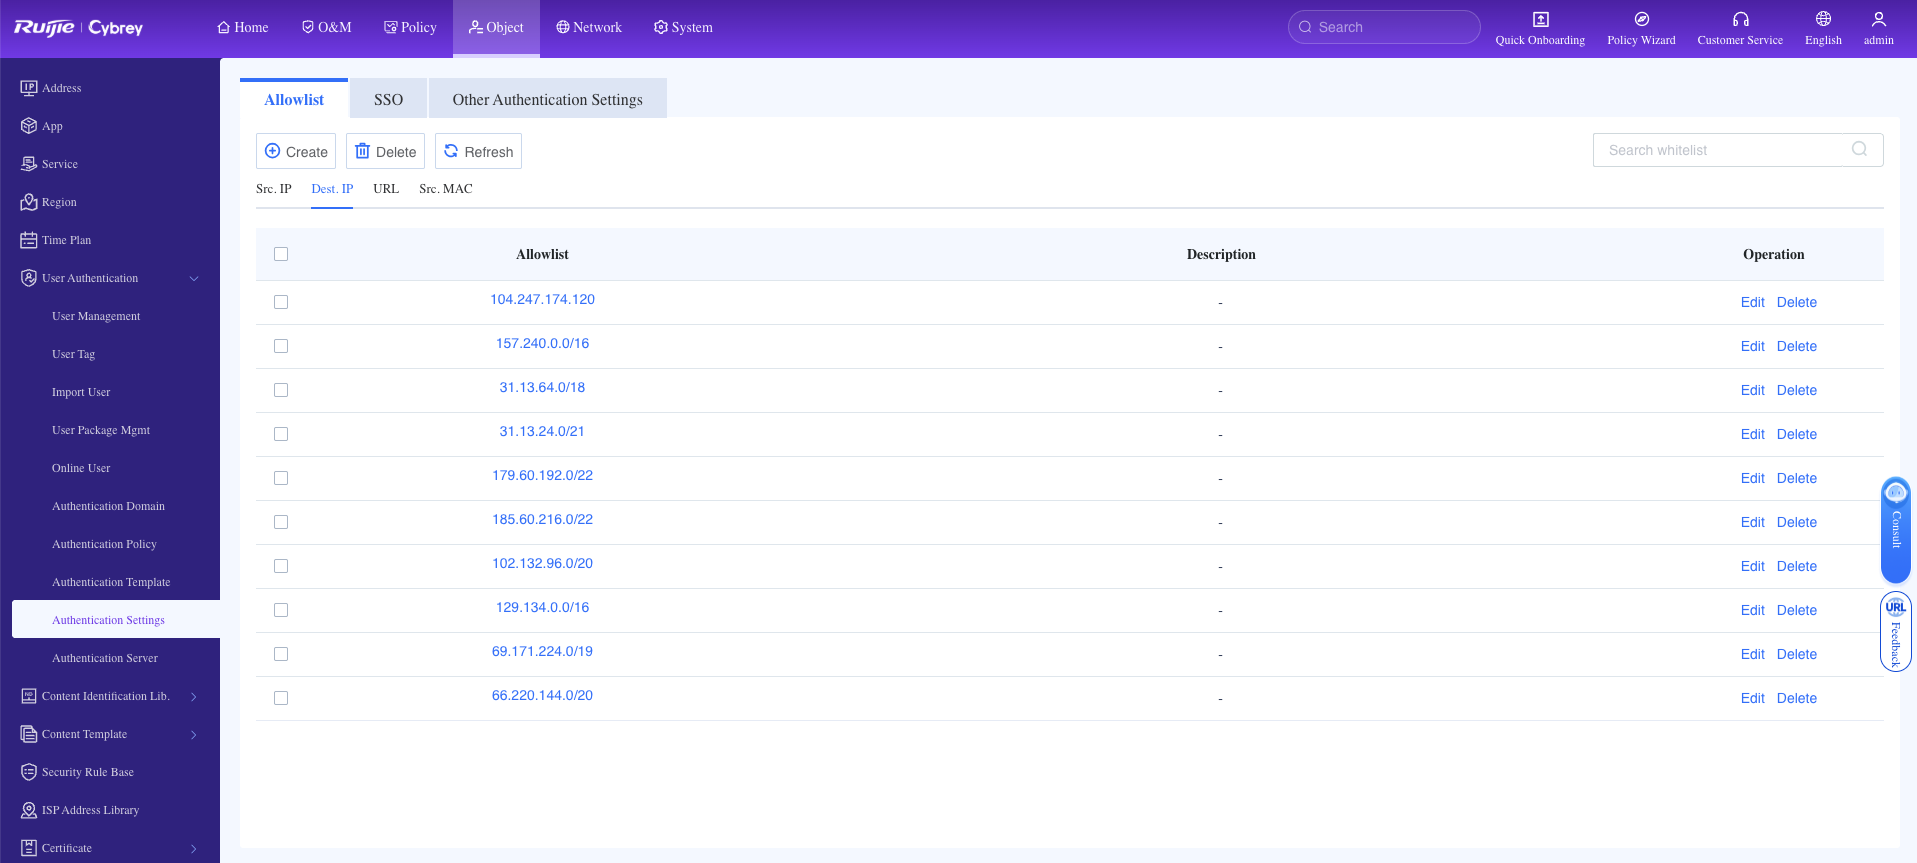
---
### **3 - Allowlist settings for trusted domains (Allowlist → URL)**
Switch to the **URL** tab in the same menu. Add `*.useroam.com` to the allowlist — guests must be able to reach it *before* they authenticate. Also define URL rules for the messaging and operating-system captive-portal detection domains that mobile devices use to verify the hotspot network in the background (for example the WhatsApp networks).
---
### **5 - Authentication policy (Edit Authentication Policy)**
As the final configuration step, go to **Authentication Policy** in the left menu and either add a new rule or edit your existing guest policy:
- **Name:** `useroam`
- **Enabled State:** set to **Enable**.
- **Src. Security Zone:** select the zone your guest network belongs to (for example `Guest`).
- **Src. Address:** `any`
- **Authentication Action:** tick **Authentication**.
- **Authentication Template Name:** select the `useroam` template you created in the previous step and save.
---
### **6 - Forwarding logs to Useroam (Syslog config)**
So that guest internet traffic and hotspot session activity can be legally signed under Turkish Law No. 5651, the logs must be forwarded to the Useroam Cloud server. In the Ruijie management interface go to **Advanced > Syslog** and use the **Add** button to define a new syslog server:
- **Syslog Server Status:** set to **Enable**.
- **Server IP:** enter the Useroam Cloud IP address `104.247.174.120`.
- **Server Port:** `514` (the default syslog port).
---
### **7 - Enable traffic reporting (Real-Time Traffic)**
In the Ruijie management interface go to **Monitor > Network > Traffic**. On the **Real-Time Traffic** tab, switch **Real-Time Traffic** on.
**Why is this required?** Without these two switches the device cannot report guests' download and upload traffic to Useroam, and traffic shows as 0 on the **Active Guests** screen in the panel.
---
#### **Important — integration complete**
That's it. Useroam Cloud Hotspot and the legal 5651 syslog integration are now fully configured on your Ruijie / Reyee gateway. Remember to update the Useroam panel whenever the device serial number or WAN IP address changes, otherwise the integration will stop working. For assistance during the process, contact our technical team at **destek@useroamteknoloji.com**.
---
## Login with WhatsApp — firewall allowlist (walled garden)
For the **Login with WhatsApp** flow to work while the guest is still behind the captive portal (before internet access is granted), the following addresses **must be allowed** in your firewall or walled-garden configuration. Without these rules the WhatsApp login screen will not open and the automatic login based on delivery confirmation will not work.
### Domains to allow (FQDN)
- `*.wa.me`
- `*.whatsapp.com`
- `*.whatsapp.net`
- `g.whatsapp.net`
- `mmg.whatsapp.net`
- `fbsbx.com`
- `*.useroam.com`
### IP addresses to allow
- `157.240.0.0` — Meta / Facebook network block
- `31.13.0.0` — Meta / Facebook network block
- `104.247.174.120` — Useroam panel
**Note:** `157.240.0.0` and `31.13.0.0` are typically `/16` network blocks (Meta infrastructure); we recommend defining them as blocks in the firewall (`157.240.0.0/16`, `31.13.0.0/16`). `104.247.174.120` is the Useroam panel IP (`/32`). Use the domain list if your firewall supports FQDN-based filtering; otherwise use the IP blocks.
# Sophos API Connection
> **Current guide:** the up-to-date step-by-step guide is on the [Sophos Firewall API Setup](https://help.useroam.com/books/settings/page/sophos-firewall-api-setup) page. This page only summarises the three basic steps on the Sophos side.
Useroam uses the Sophos Firewall API to create and remove hotspot user sessions automatically. This page shows how to create the API user and grant the API permission on the Sophos side.
> **When do I need this?** Complete these steps after the **Sophos Integration Guide**, whenever Useroam has to manage users over the API.
---
### Creating a new profile
In Sophos, go to **Profile > Device Access** in the left menu and create a new profile. Grant all permissions.
[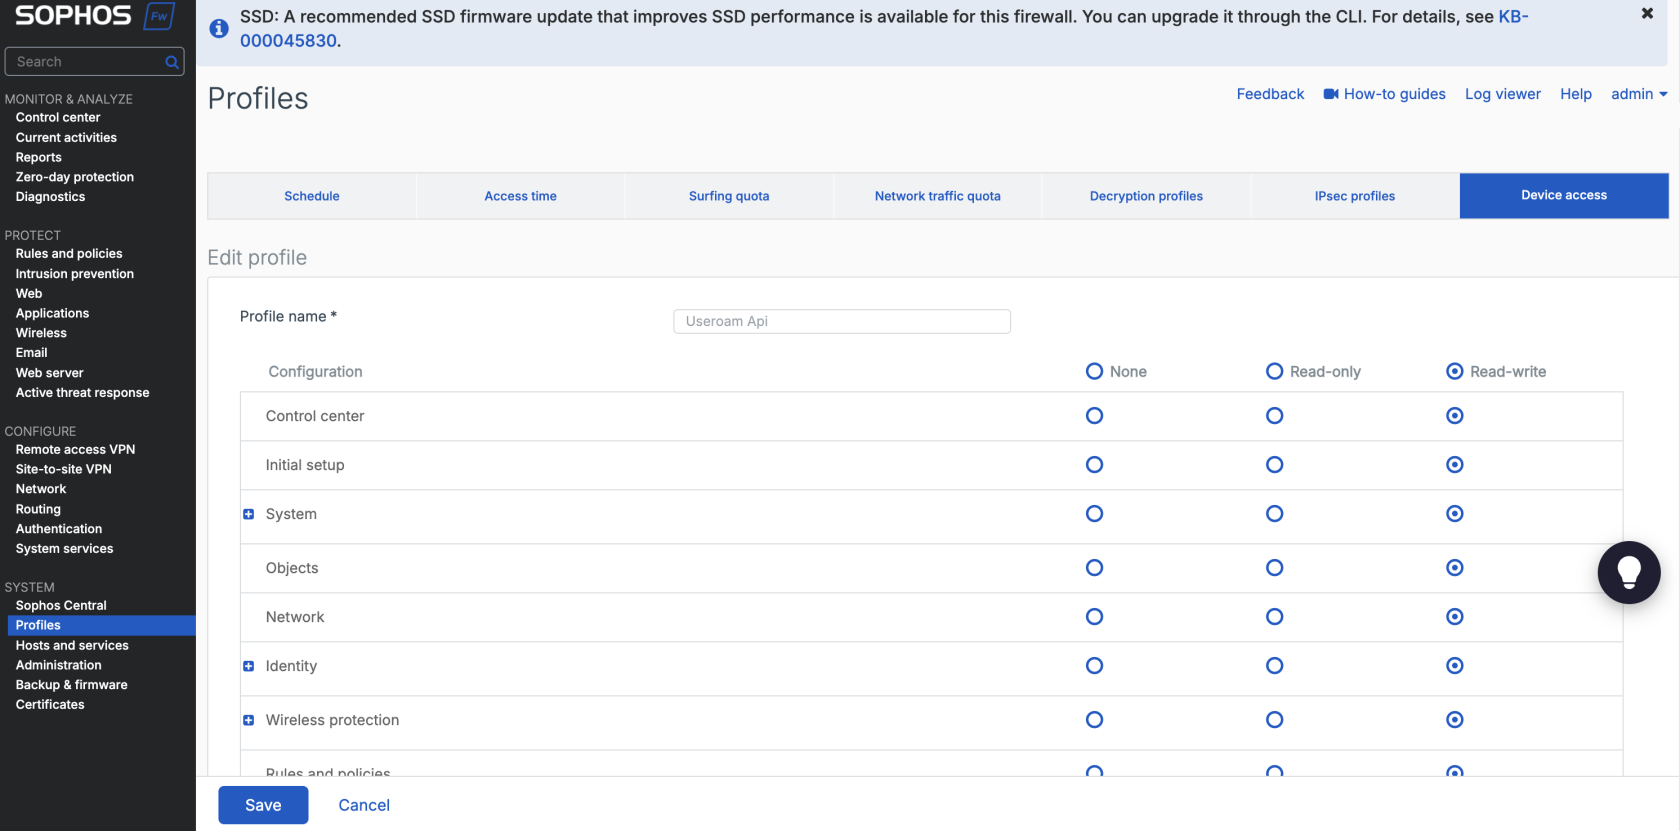](https://help.useroam.com/uploads/images/gallery/2026-09/sophos-api-profil.png)
---
### Creating the API user
In Sophos, go to **Authentication > Users > New user** in the left menu and create a new user. For **User Profile**, select the profile you created in the previous step.
[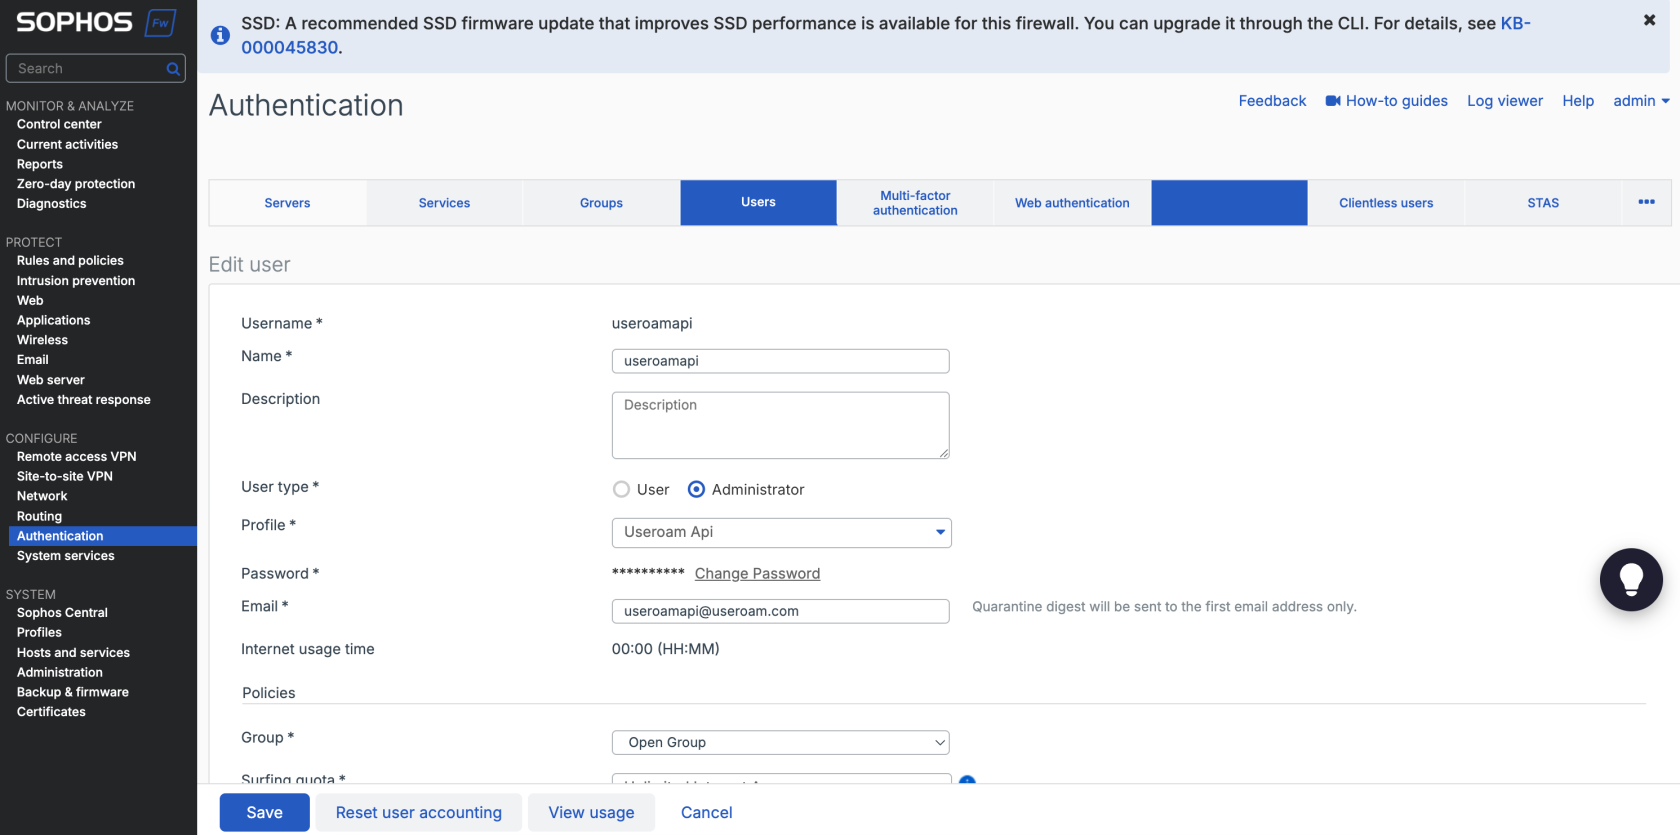](https://help.useroam.com/uploads/images/gallery/2026-09/sophos-api-kullanici.png)
---
### Granting the API permission
In Sophos, open **Backup & Firmware** from the left menu, switch to the **API** tab, add the entry below to the **API Configuration** field and click **+**.
[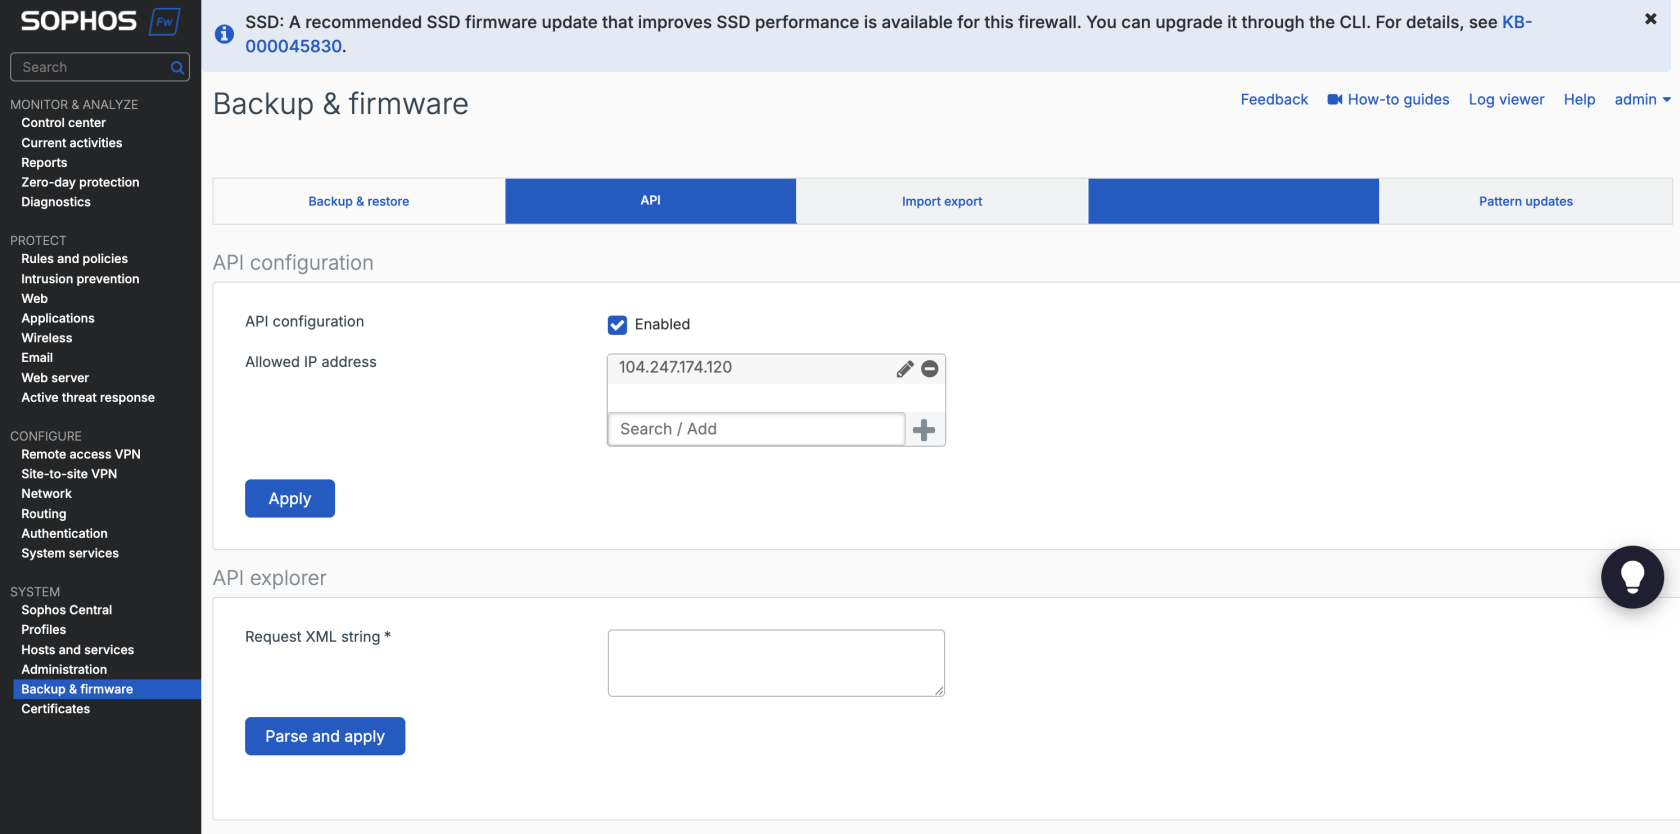](https://help.useroam.com/uploads/images/gallery/2026-09/sophos-api-izin.png)
> **Tip:** the API user's credentials must match the ones entered on the device record in the Useroam panel. If you change the password later, update it in the panel as well.